How to Check a URL for Malware: Spot the Warning Signs Before You Click


Blog Overview: To check URL for malware it is not necessary to open it. You can check a URL for malware by:
- Scanning it safely.
- Examining real domain.
- Following redirects.
- Reviewing reputation signals before visiting destination.
This guide will show you what to check, what different scan results mean, and when URL demands deeper and more serious investigation.
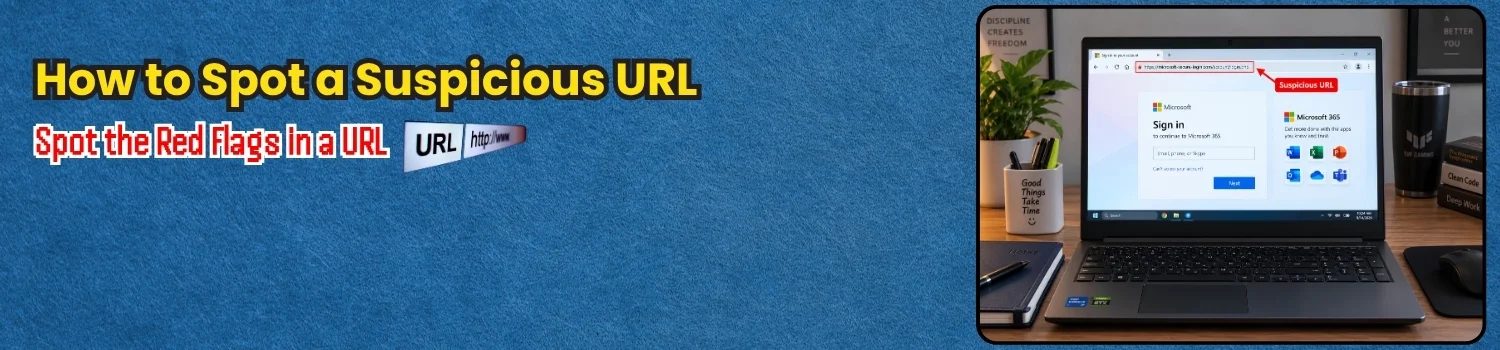
Quick Answer: To check a URL for malware.
- Copy link without opening it,
- Paste it in a trusted URL checker.
- Review response.
- Inspect URL’s domain, redirects, reputation, and other warning signs.
Never treat HTTPS or “clean” result alone as proof that website is safe. Link can look ordinary and safe but it can lead somewhere dangerous. Familiar brand name, convincing email, small padlock icon can look and make you feel that URL is safe. As user you should not click first and investigate later. Careful URL check lets you examine link before you expose your browser, credentials, or device to destination.
How to Check a URL for Malware
Safest process is:
- Collect the URL
- Scan it
- Inspect what scanner found,
- Decide what to do not before scanning.
Think of it like checking package label before opening the box. You want to know where it came from before you want to see what is inside.
1. Copy and Scan the URL Safely:
Start by copying full URL without opening the page. On desktop, you can right-click a hyperlink and choose Copy link address. On mobile, press and hold the link and use copy option.
Then paste the URL into a reputable checker. Useful services include Google Safe Browsing, Bitdefender Link Checker. These services can provide threat-related information, but their reports should be interpreted. Not to be treated as absolute guarantees.
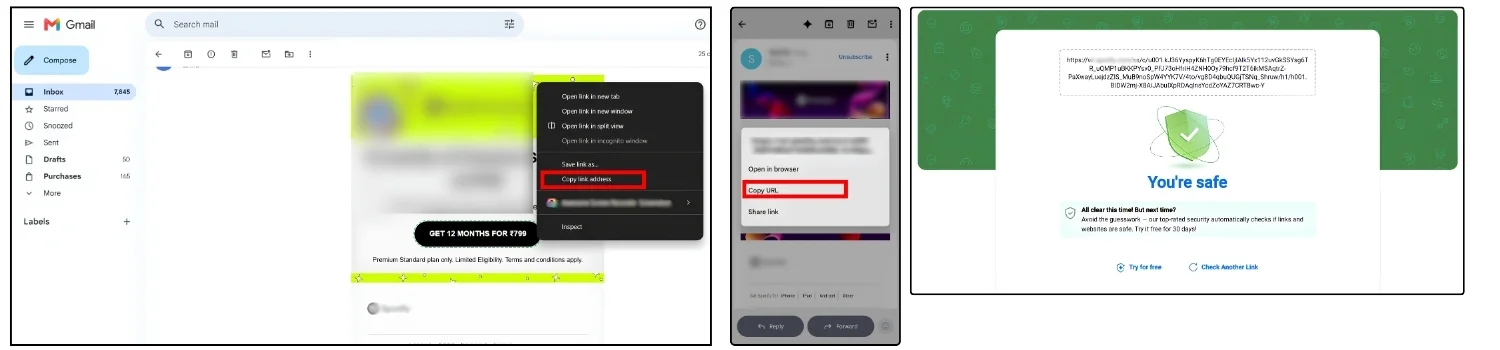
Important privacy check: Do not blindly submit URLs containing password-reset tokens, session IDs, private document links, and other sensitive information to public scanners. URL can contain information that was not meant to be publicly shared.
2. Inspect Real Domain:
URL can contain trusted brand name without belonging to that brand. This is very important thing to understand when you check link for malware.
Consider: https://login.rmicrosoft.com.example.xyz/account Quick scan may make it look like “Microsoft” read carefully- it’s written “rmicrosoft”. Look from right to left when identifying registered domain. The subdomain and path can contain convincing words, but they do not change who controls domain.
Look for Lookalike Domains: Attackers create addresses that looks like real brands. Single changed character is enough:
- micros0ft.com
- paypa1.com
- amaz0n-support.com
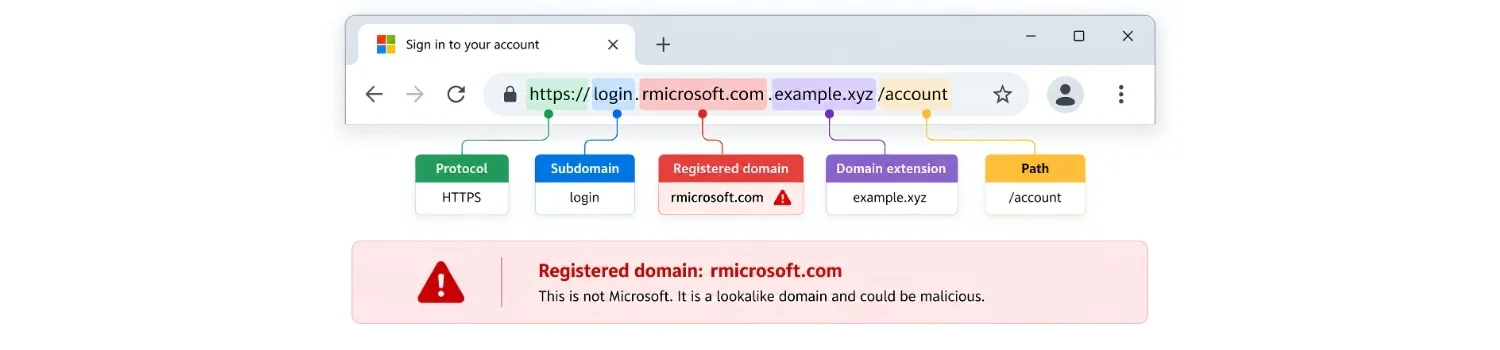
These are not automatically malicious just because they look unusual, but they need closer inspection. Typosquatting, brand impersonation, email impersonation, unexpected subdomains, and extra words can look like familiar company name but when inspected closely these are useful warning signals. Read part after domain can provide context. Long strings of confusing characters, different parameters, or links designed to hide real destination deserve attention.
3. Check Redirects, Reputation, and Verdict
Possibility is that, received URL may not take you directly to the page you expect. It can travel through multiple destinations first.
For example: Link A, Redirect B, Redirect C, Final Site
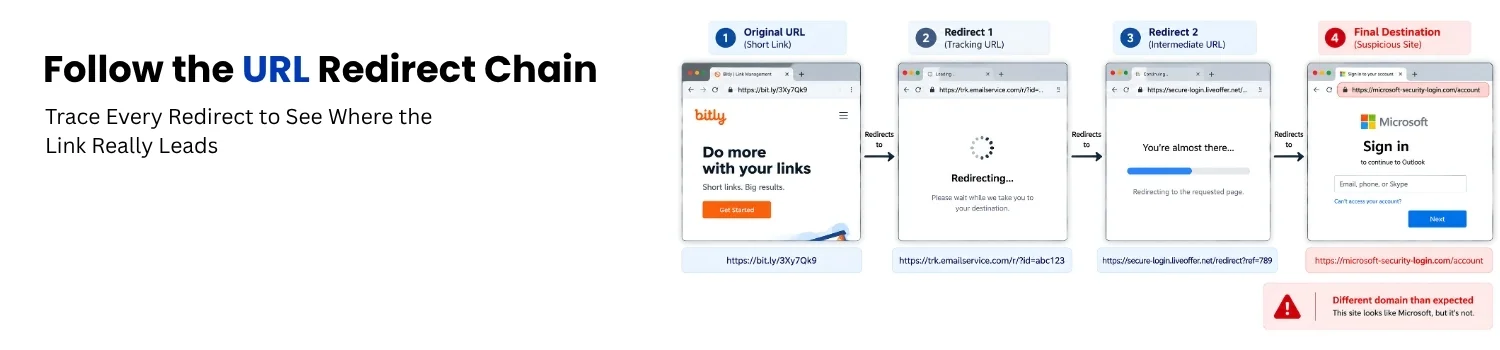
That is because visible link and final destination tell two different things.
Check the Redirect Chain: Short link, tracking link, or redirecting URL is not automatically malicious. But redirects deserve attention, when final destination has different domain, asks for credentials, or attempts a download.’
Understand Scanner Verdict: Scanner can show you results such as:
| Result | What it Usually Means |
|---|---|
| Malicious | Strong evidence of harmful or deceptive activity. |
| Suspicious | Risk indicators exist, but evidence may not be conclusive. |
| Clean / Safe | No known threat is detected. |
| Unknown | Service has limited information. |
Do not confuse clean with guaranteed safe. Brand-new phishing page may not have enough reputation history or detection coverage to trigger a warning immediately. The right question is not only “Did the scanner say safe?” It is “What evidence supports that result?”
4. Combine Warning Signs
One strange character do not means URL is malicious. Five signals together are more meaningful.
| What You Notice | Why It Matters |
|---|---|
| Lookalike Brand Domain | Indicates Impersonation. |
| Unexpected Redirect | Can hide final destination. |
| Credential request | Indicates phishing. |
| Poor domain reputation | Can point to previous threat activity. |
| New and unfamiliar infrastructure | Provide additional context. |
| Suspicious download | Can indicate malware delivery. |
| URL do not match the message | Can indicate deception. |
This is the reason to check a URL for malware. URL malware checker should only be treated as one single source evidence not the entire investigation.
Do Not Trust HTTPS Alone: HTTPS is useful because it encrypts communication between your browser and website. It doesn’t tell you that website itself is legitimate.
- Phishing website can use HTTPS.
- So a newly created malicious website.
Think of HTTPS as locked conversation between you and site, not a certificate of good character.
Clean Result Is Not the End
Threat detection changes with time. URL that looks clean today later identified as phishing or malware-related after behavior changes, its infrastructure is reported, and more threat intelligence becomes available. That is reason context is very important.
If URL has arrived in:
- Unexpected invoice.
- Password-reset message.
- Delivery notice, or account suspension email.
Do not ignore the because one scanner returned a clean result.
5. Know When URL Analysis Is Not Enough
This is where URL checking becomes part of big investigation. Think you receive email saying:
“Your Microsoft 365 account will be suspended today. Verify now.”
Message contains suspicious URL. The process you will follow is to, check URL, inspect domain, check redirects, review reputation. That is useful. But investigator still need to answer:
- Who sent the message.
- Sender address spoofed or not.
- Similar emails sent to other people as well
- What headers accompanied the message.
- Same URL found in other evidence.
- When message arrived.
- What other indicators are connected to incident.
6. Safer Way to Handle Suspicious URLs
When you see a suspicious link, safest sequence is simple:
- Do not click it.
- Copy the URL without opening it.
- Scan with reputable checker.
- Inspect the domain and redirect path.
- Review reputation and verdict.
- Consider context in which you received it.
- Escalate to deeper investigation when the URL is part of an email incident.
How to Check URL for Malware Through Advanced Software?
It is important to know how to analyze URLs for malware, but it is always important to check through advanced techniques. This is so because this technique not only analyzes the URL for malware but also provides you with more advanced features for email forensics examinations.
MailXaminer is an advanced email analysis software that can make your investigation of emails more advanced. This URL checker is designed to make digital investigations by offering powerful email search, IP analysis, and recovery capabilities. This is specially designed to be equipped with advanced algorithms that enable forensics experts to perform email metadata analysis.
Advanced URL Analysis Feature to Detect Phishing Attacks
This software allows investigators to thoroughly analyze URLs embedded in emails for phishing email forensics investigations. The software applies multiple layers of analysis.
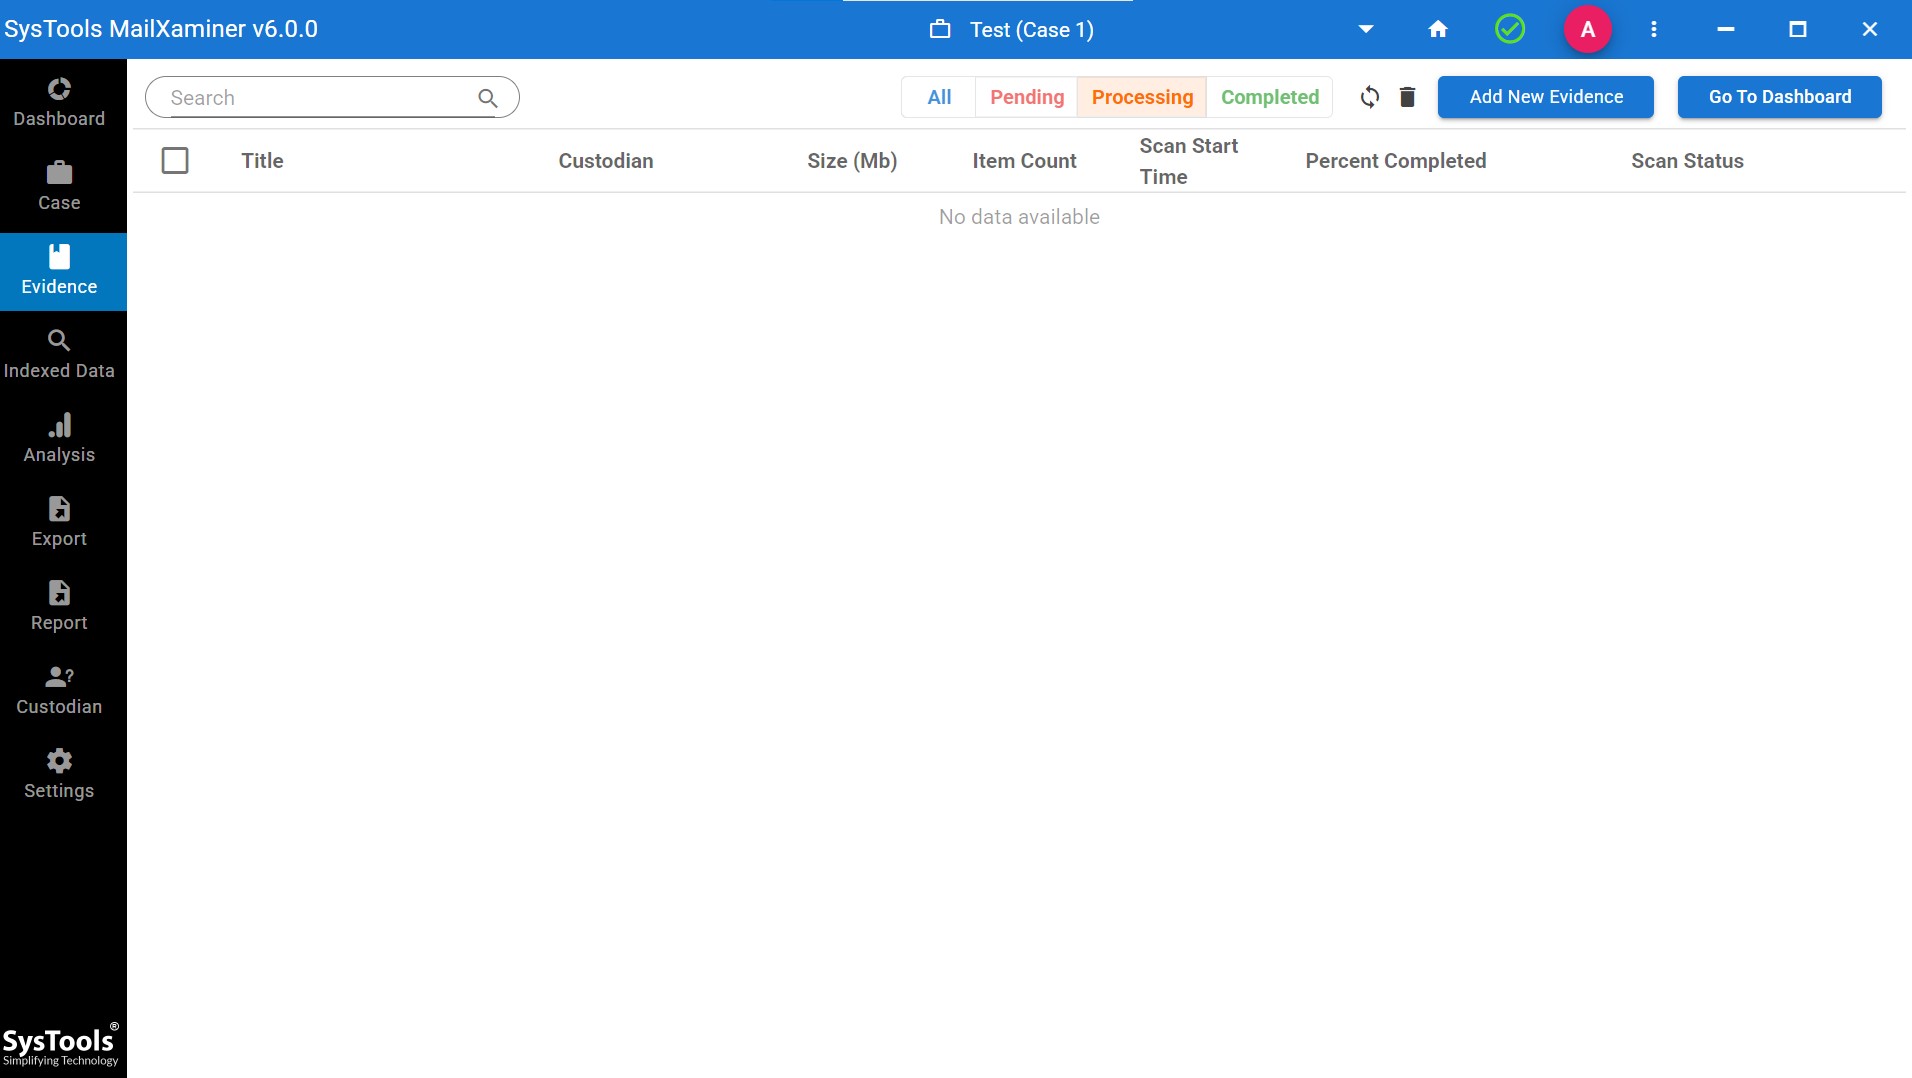
Step 1. Create a new case and add new email evidence.
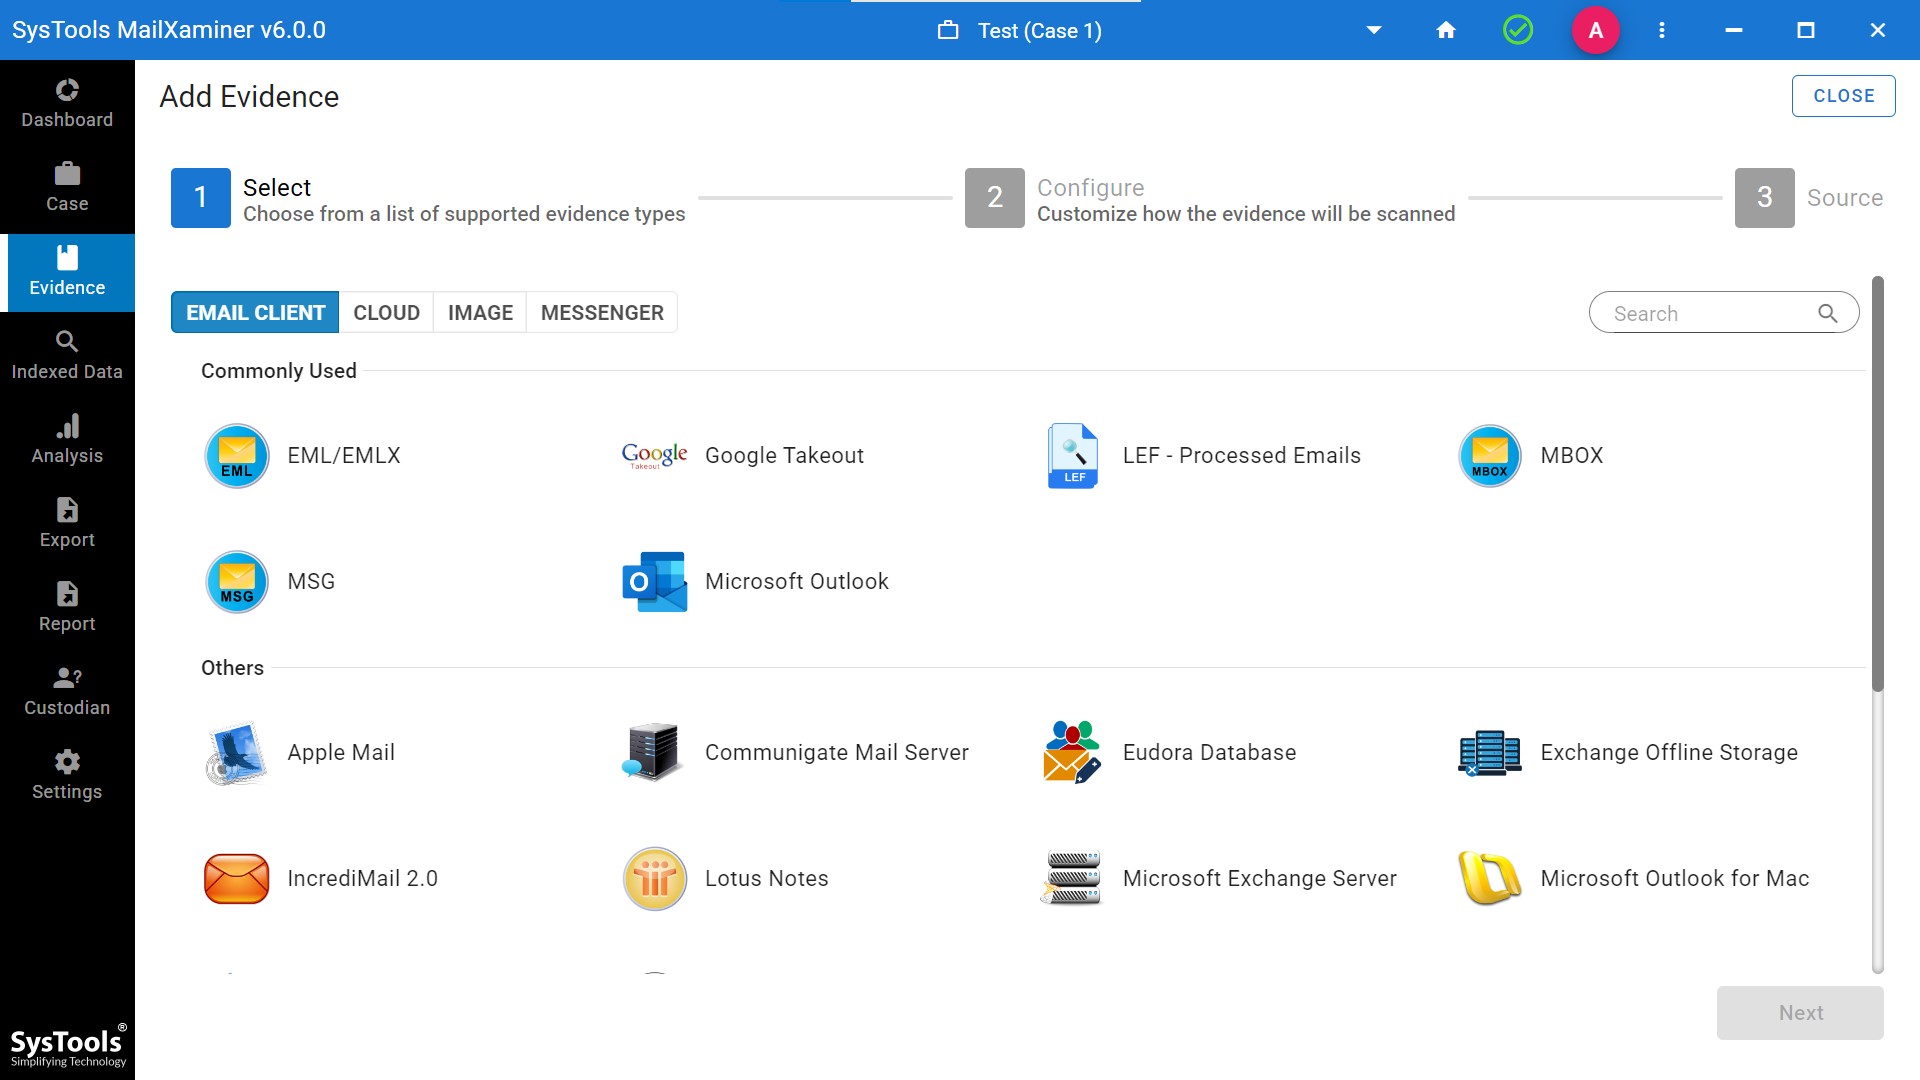
Step 2. Then, choose the email source to analyze URL for malware.
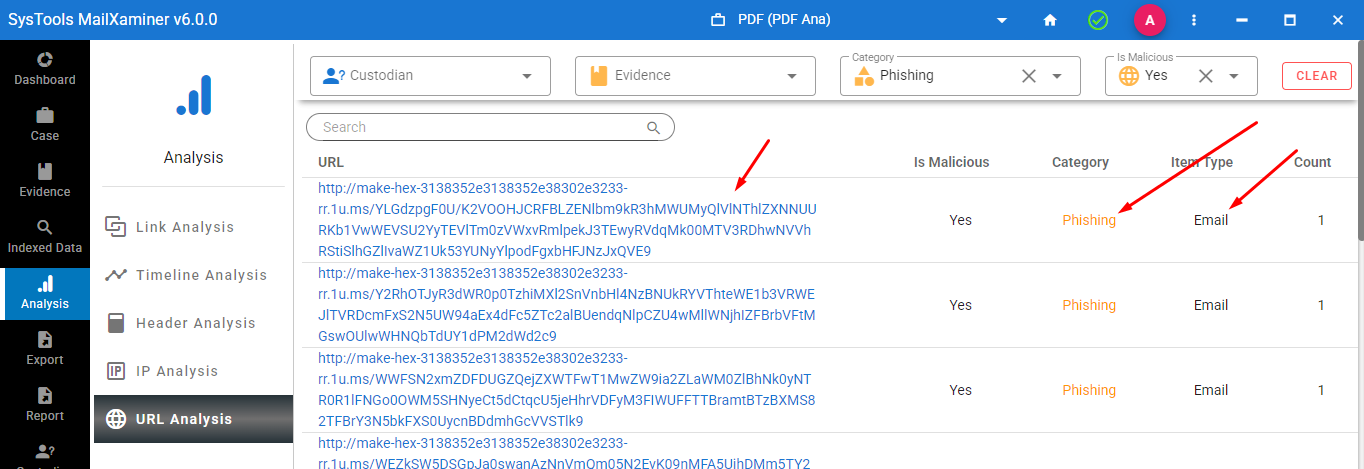
Step 3. After adding various cases, this malicious URL scanner analyzes and detects the categories, mentioning malicious, category, item type, and total case count.
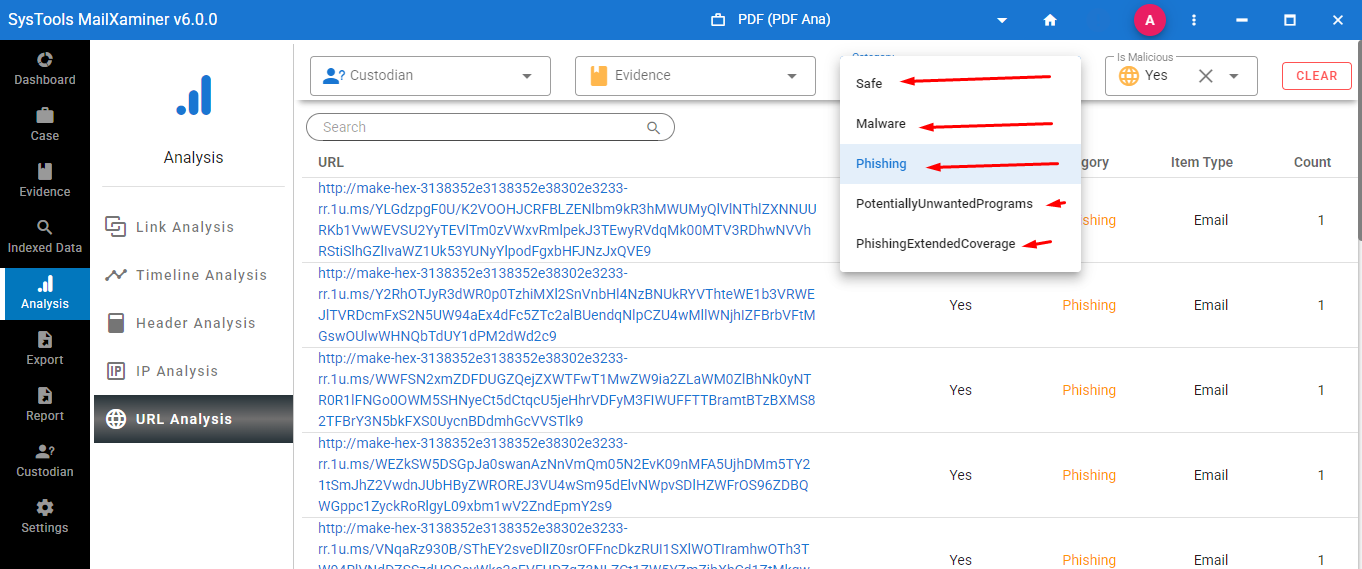
Step 4. Through this URL analysis feature, you will get a complete report of all the malicious URLs.
Conclusion
In this modern age of technology, defending your personal information requires understanding how to check URLs for malware. To trick recipients into downloading dangerous files or disclosing private information, cybercriminals frequently hide malicious links in emails. It becomes a task for investigator to find hidden URLs in phishing emails. Identity theft, financial damages, or even an entire system compromise may result from these threats. You need to check emails and also frequently check suspicious email attachments.
Thus, maintain yourself against online threats by following the instructions in this guide and utilizing legitimate techniques, and use the best URL checker to perform URL analysis. Suspicious URL should never be judged by appearance alone. Better approach is to inspect URL before opening it, scan for known threats, understand its domain and redirects, and interpret the result with context in which link appeared.
Everyday link checking, a reputable URL checker can be a useful first step. For email-related incident, the URL may be only one piece of a much larger evidence set.
Frequently Asked Questions
Q – How do I check a URL for malware ?
A – Copy URL without opening it, scan it via trusted URL checker, and review its domain, redirects, reputation, and security verdict.
Q – Can a URL be malicious even if it uses HTTPS ?
A – Yes. HTTPS encrypts connection, but it do not prove that website is legitimate, trustworthy, and free from malware.
Q – What are signs of a malicious URL ?
A – Lookalike domains, suspicious redirects, unusual URL structures, unexpected login requests, and poor reputation or threat intelligence results.