General Search Technique To Search Digital and Email Data


Overview: Email Search Techniques help investigators locate relevant emails, narrow large collection of evidence and find information that is required in an investigation. One of the most useful technique is General Search, this lets you search by keyword and build more detailed queries using fields, conditions and logical operations.
There are six search methods available in MailXaminer:
- General Search
- Fuzzy Search
- Wildcard Search
- Regex Search
- Proximity Search
- Stem Search.
Each serves different purpose. In this guide we will focus on purely general search and explains how to move from simple keyword search to structured query with multiple groups.
Think of investigating emails related to suspicious invoice, containing thousands of messages. Opening every email will be time-consuming. Well constructed and highly targeted search can help you narrow the collection and focus your review on messages that match investigative requirements.
It is just like ordering food for delivery. There may be hundreds of restaurants and dishes to choose from and checking every menu would take time. Instead you can select cuisine, choose vegetarian option and set delivery time of under 30 minutes. Each filter will remove options that do not match your requirements and provides you more focused and relevant list.
Let’s begin with simple search and build more advanced one.
What Is General Search?
General search helps in finding emails by: entering keyword or combining conditions that portray messages you want to locate. You can start with single search term and then add more rules to your search when you need to narrow down results. General Search offers two practical approaches:
- Keyword Search: Enter word or term, to retrieve matching emails.
- Advanced Query Building: Combining fields, conditions, groups, and AND/OR operators to create specific search.
The first approach is useful when you know keyword to look for. Second helps when that term alone is not able to narrow results enough. For example, searching for “interested” can help in locating emails containing that keyword. If you need to find messages with attachments that also meet other criteria, you can build query using attachment-related fields and condition. Here the goal is to find emails that match your investigative requirements without unnecessarily excluding relevant evidence.
How General Search Supports Email Search Techniques for Digital Forensics
Process of General search starts with loaded email evidence in a tool. You select General Search, enter keyword or build query, apply search or review results. When one condition is not enough user can combine multiple rules into groups.
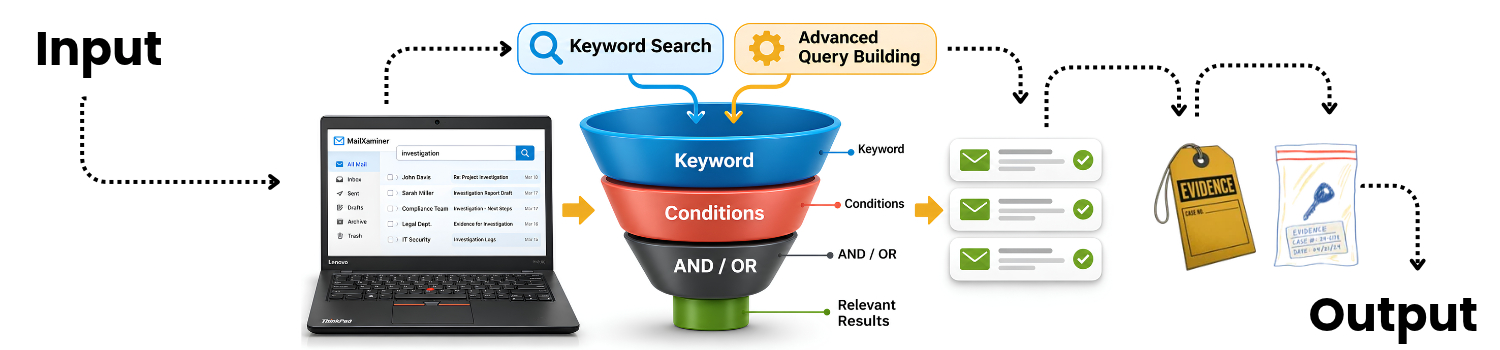
Now let us check how to perform this General search on real tool.
Type 1: Basic Keyword Search Method in General Search
Keyword search is the simplest way to begin. Enter term related to your investigation, apply the search, and examine matching emails.
Follow these steps:
-
- Upload your email evidence and ensure it has been processed and is available under Indexed Data.
- Open Indexed Data
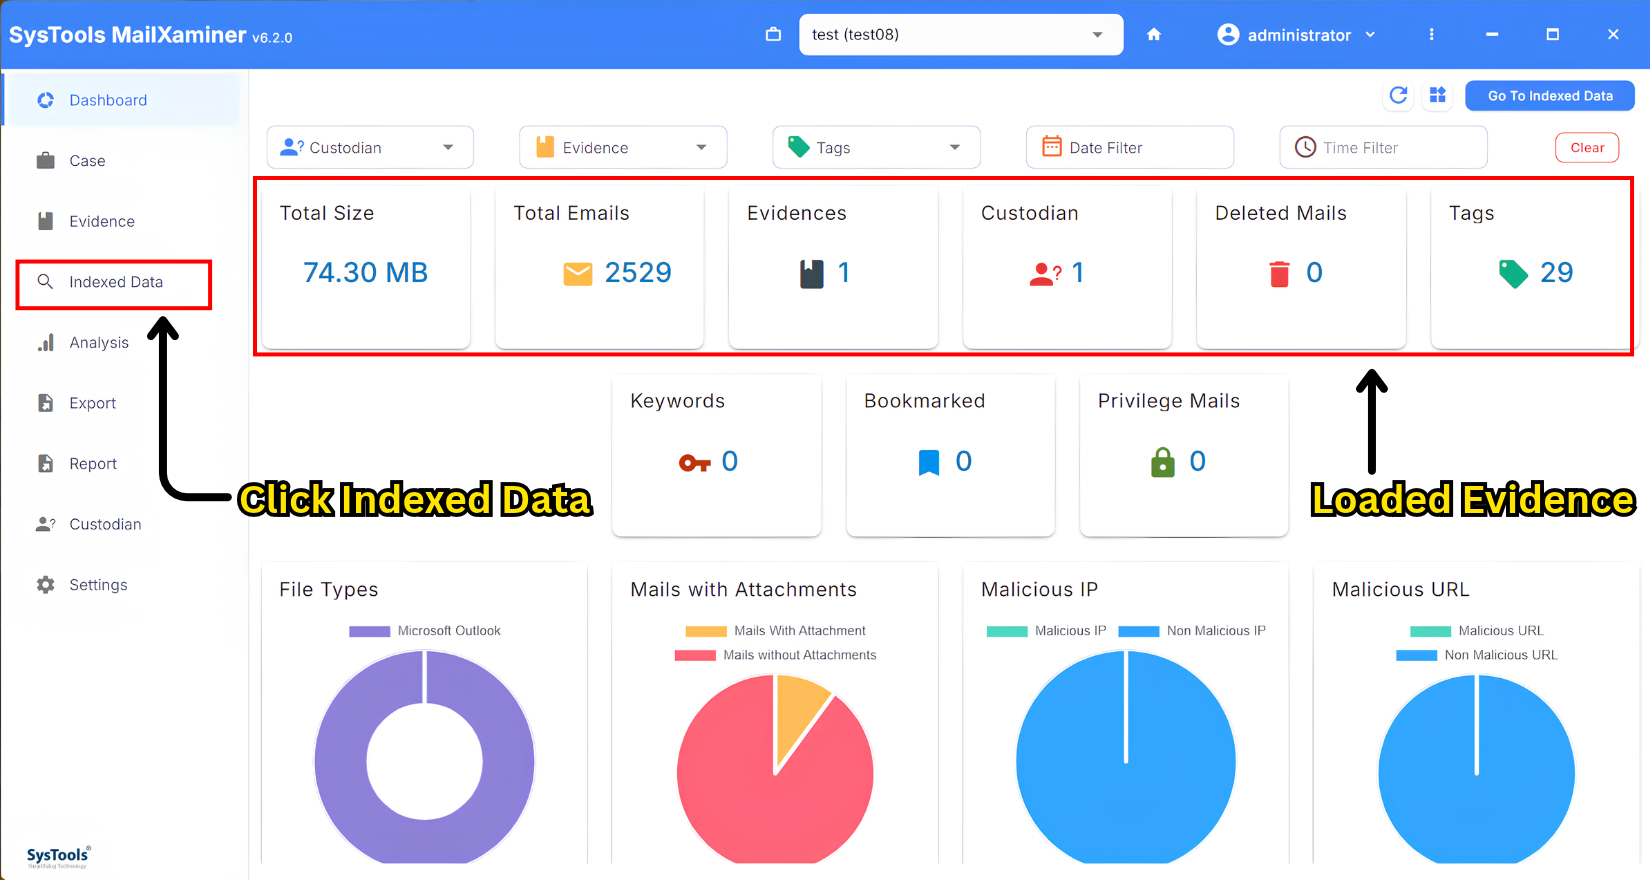
- Click on small settings icon on search bar to select General search from dropdown.
- Select General Search.
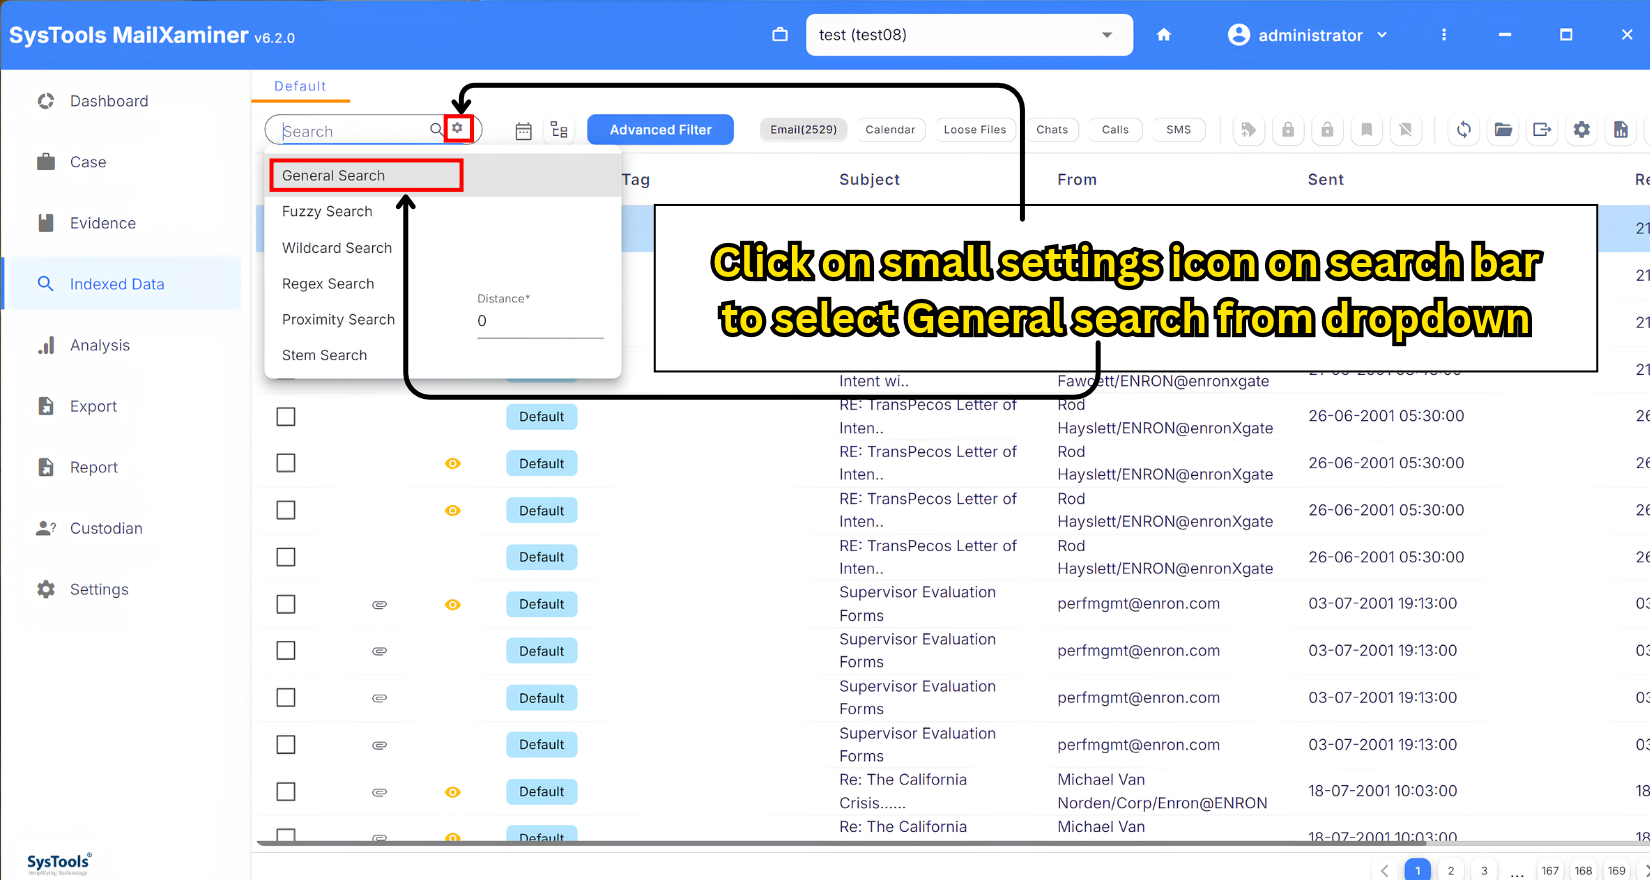
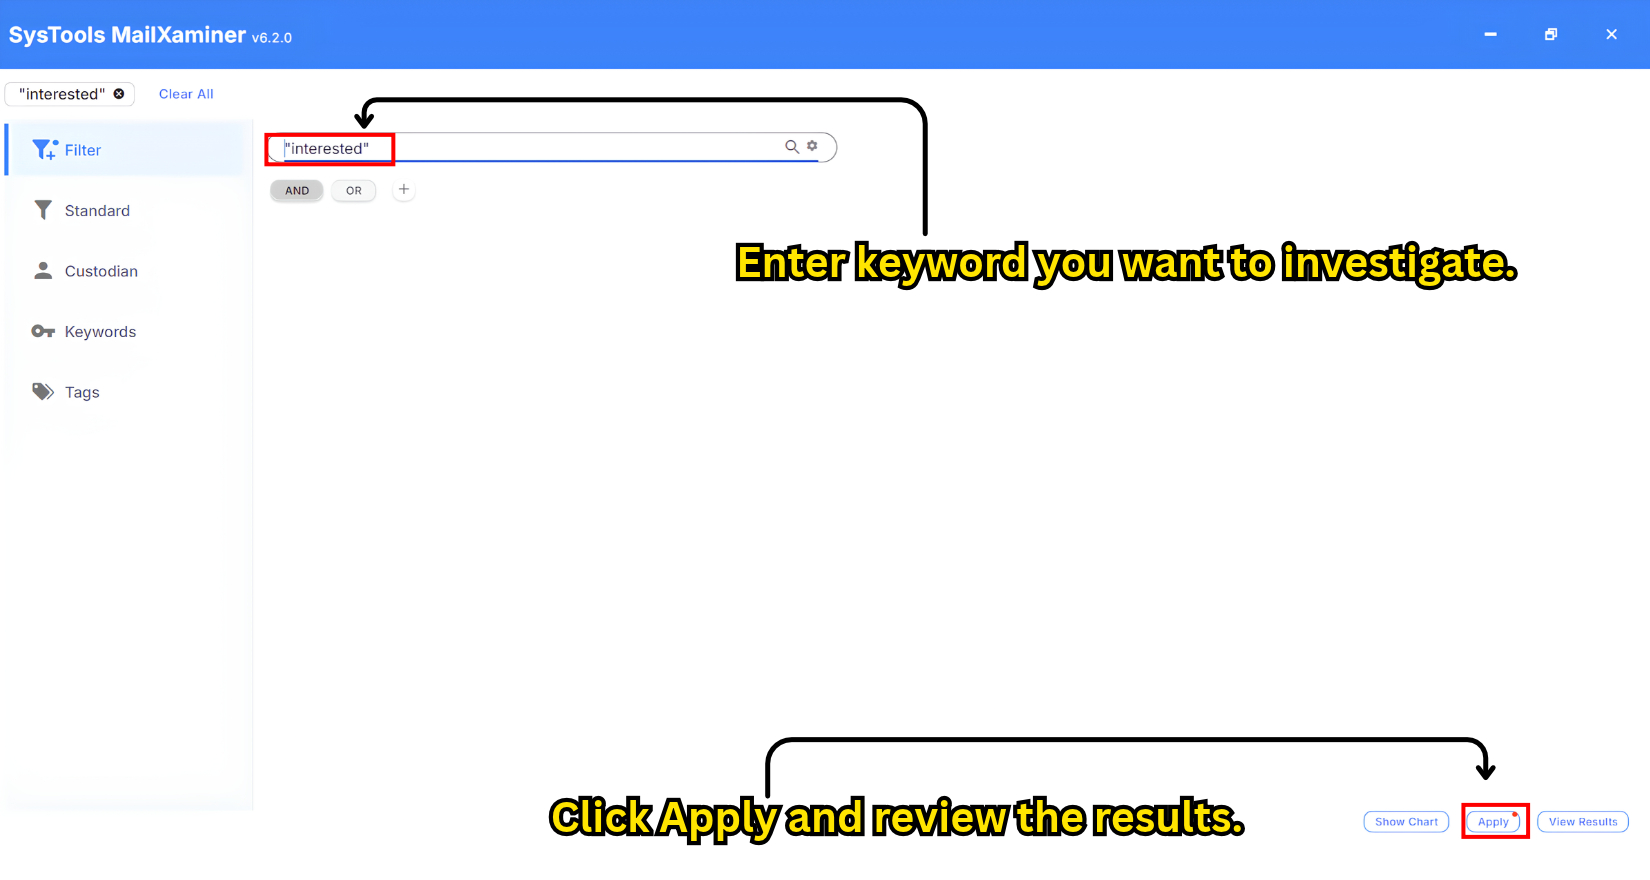
- Enter keyword you want to investigate.
For example, you want to locate messages containing word interested. Enter “interested” in double quotes in search bar and apply the search.
- Click Apply and review the results.
- Investigate output based on your keyword.
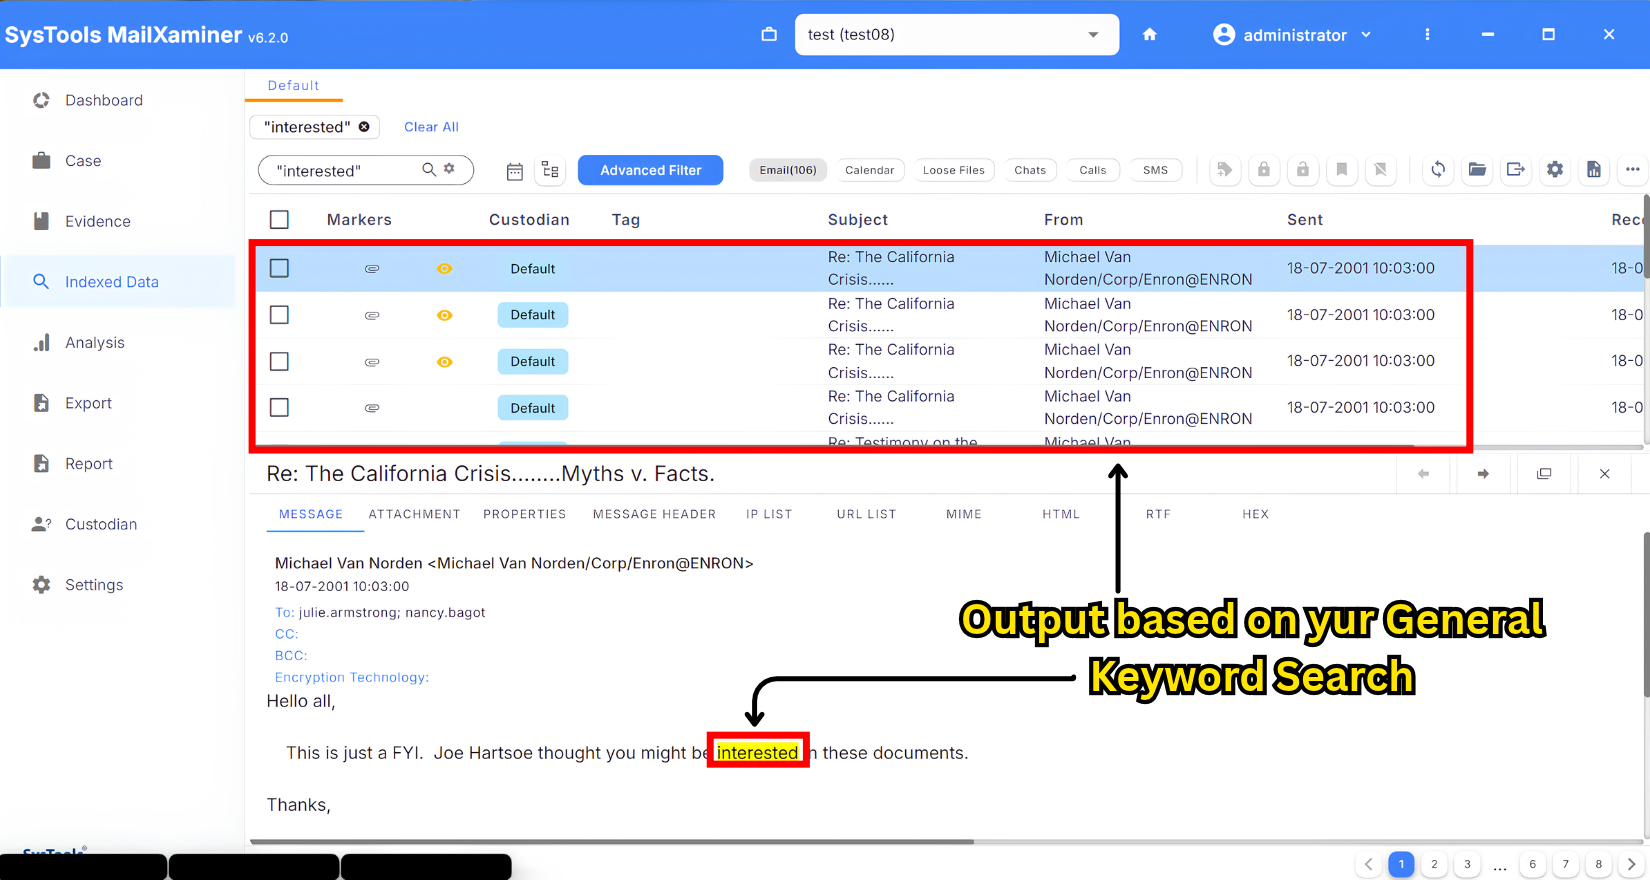
What To Do Next: Review matching emails and examine their context to determine are they relevant. Keyword match helps you locate a message, but it does not, by itself, establish what the message proves. If the results are too broad or you need to search using specific email properties, move to the advanced query builder.
Type 2: Field-Based Query Building in General Search
Field-based query lets you specify:
- Email property
- Operator that defines rule and value to check against.
This is useful when keyword alone cannot express what you want to find. To use this effectively we build a query so let us first understand what is query builder and build-up.
Query Builder: It is search interface that help investigators in creation of specific email searches by selecting fields, setting conditions, entering values, and combining them using AND and OR operators.
Query Buildup: It is simple process of combining these fields and conditions to create effective search that matches specific requirements.
Distinction: Query Builder is graphical user interface (GUI) where user creates search. Query Buildup is process of adding and combining fields and conditions in that interface to perform email search techniques.
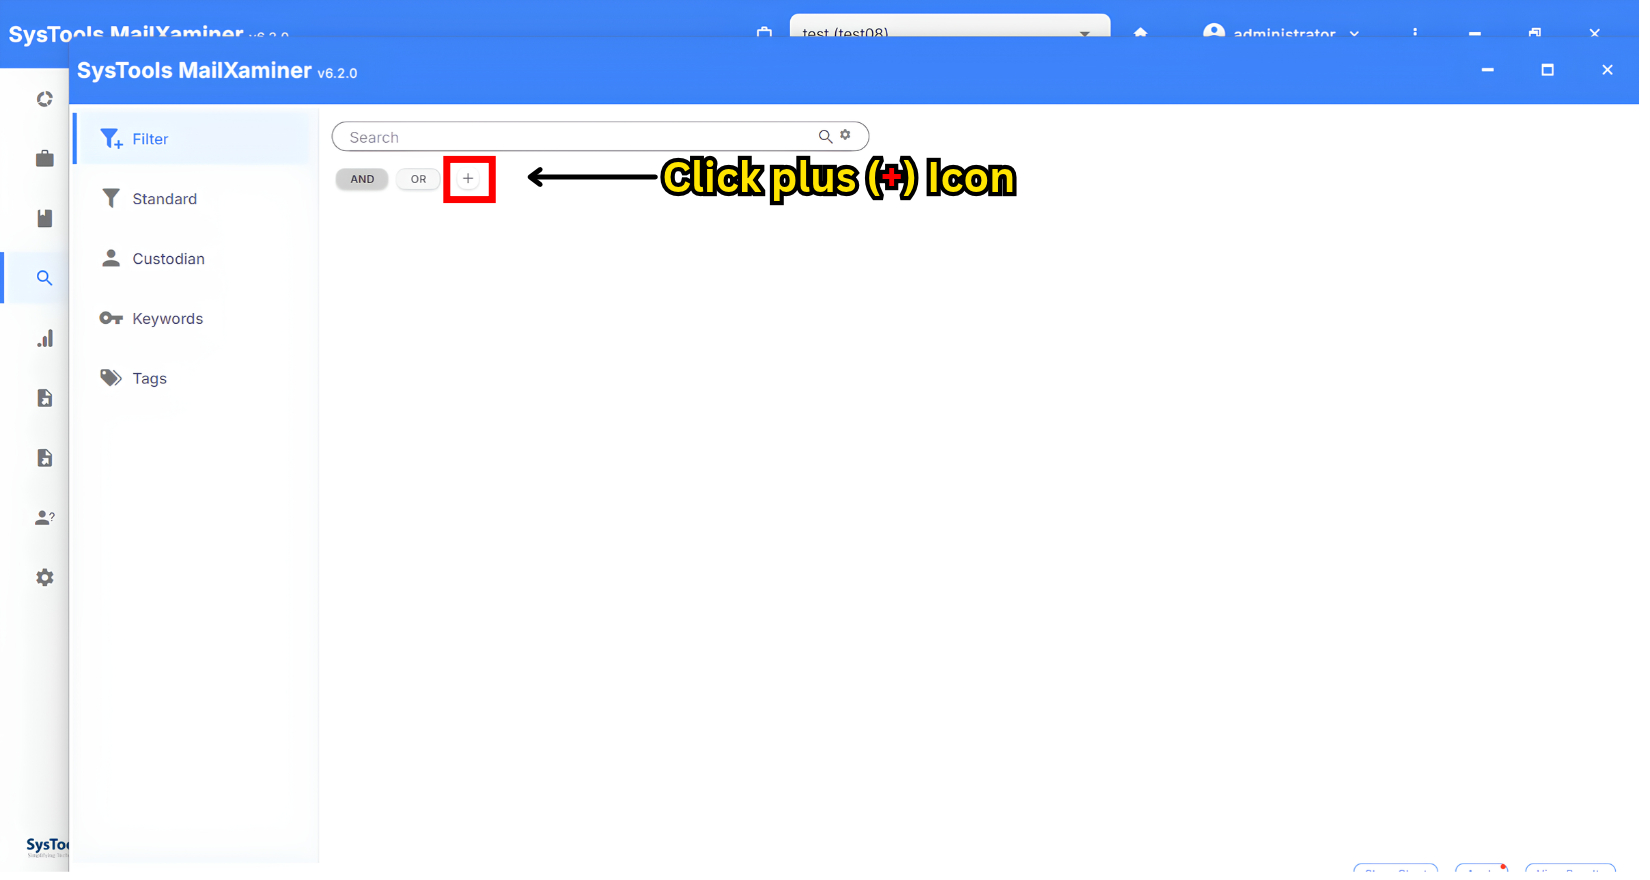
- To start, click plus (+) icon beside the AND or OR control in query builder.
- Once done menu will pop up and provides options for adding groups, conditions, and other query components.
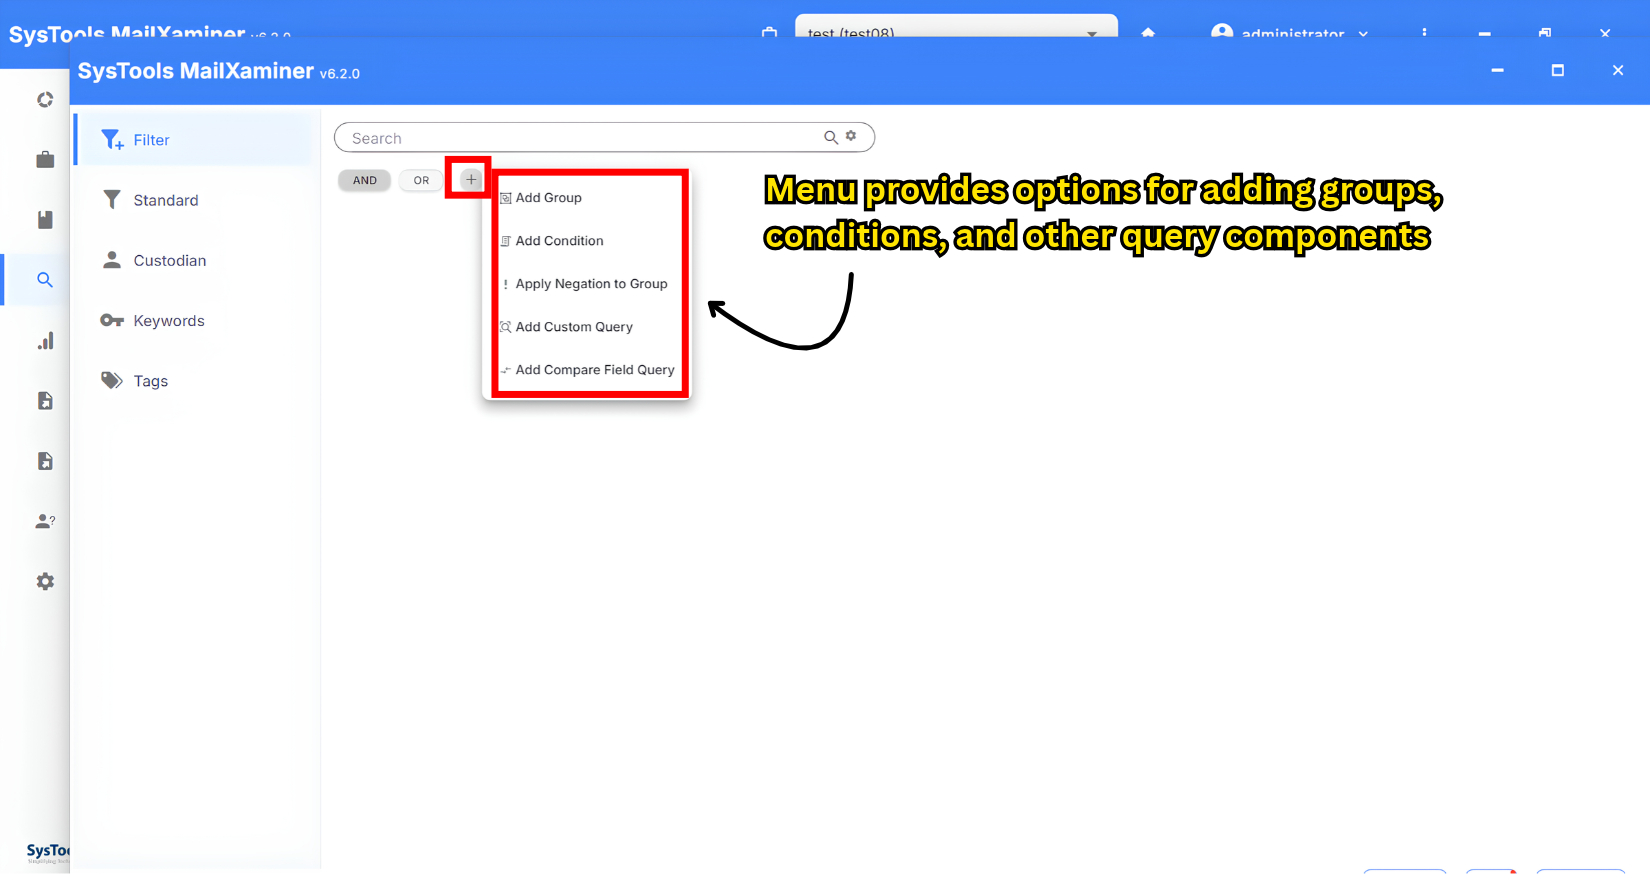
Available actions shown in interface are:
| Action | What it does |
|---|---|
| Add Group | Creates group for organizing related conditions. |
| Add Condition | Adds rule to the query |
| Apply Negation to Group | This changes selected group’s matching logic to its exact opposite. |
| Add custom Query | Add custom query using Syntax supported by tool |
| Add Compare Field Query | Provides option for building query that compares field. |
For example, consider this dummy condition for better clarity of these components:
Dummy Condition: Email Attachment Count Greater Than Or Equal to 1
Here,
- Email.Attachment Count is field.
- Greater Than Or Equal is an operator,
- 1 is value.
This condition will look for emails with at least one attachment.
For example: To show you how you can build queries like this using multiple groups and conditions see the interface just for an example we will look how to do this in detail below.
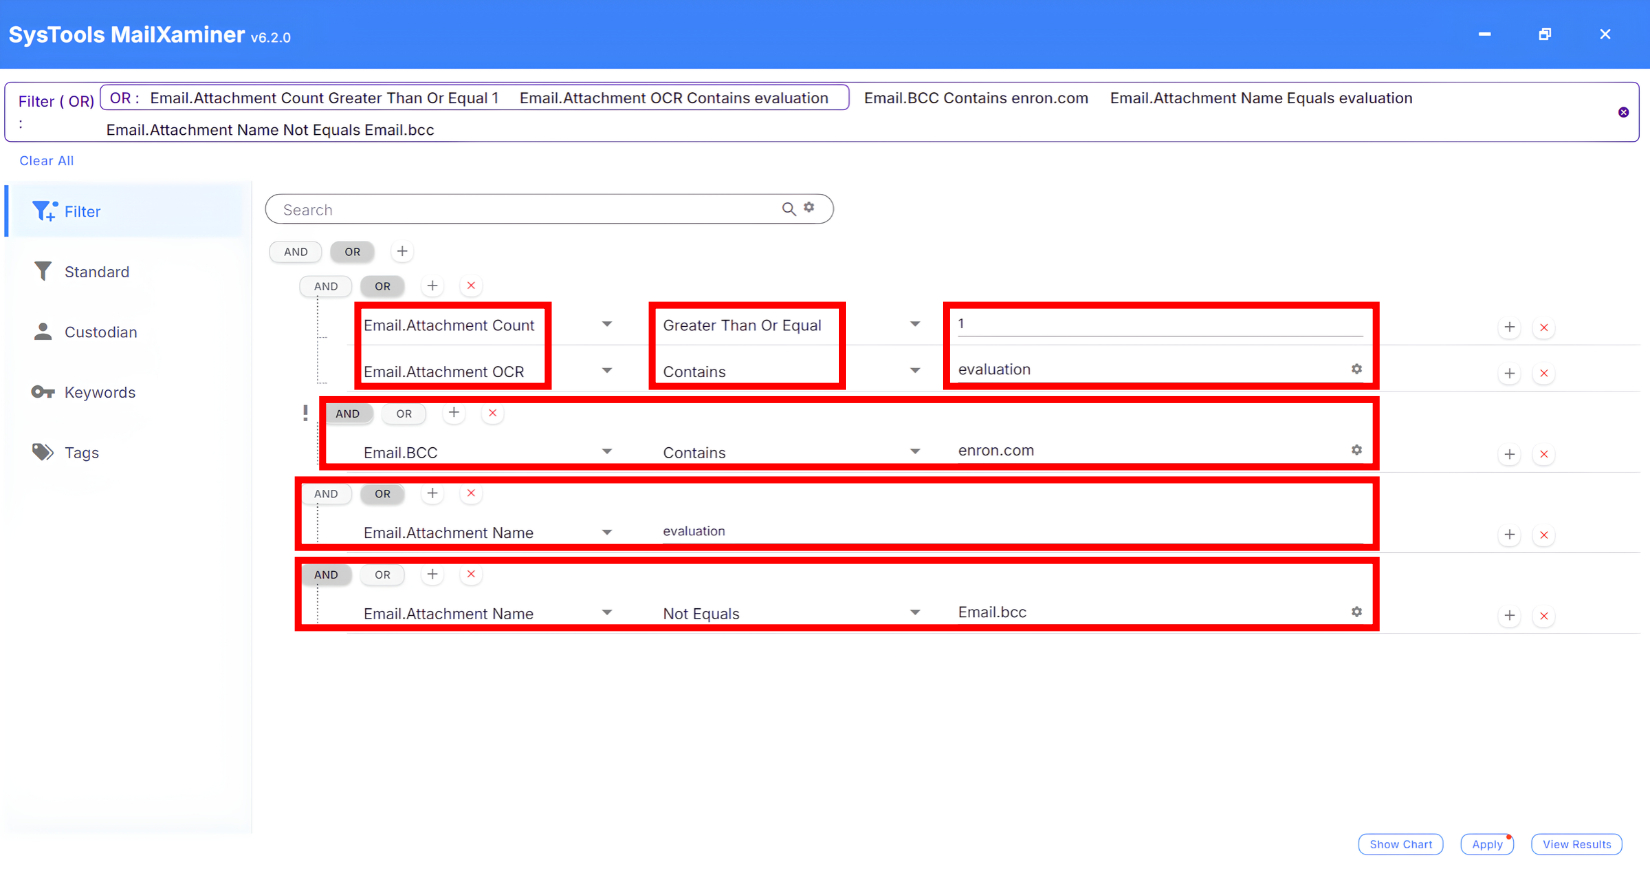
Interface also shows fields such as Email.Attachment Name, Email.Attachment OCR, and Email.BCC. Available operators will depend on selected field. Interface examples include contains,:
- Equal,
- Not Equals,
- Greater Than or Equal.
Select an operator that perfectly matches type of information you want to examine. Many investigators and professional users prefer to investigate emails through searching for information or working inside email body. Let us have a look at that.
Searching For Information Inside Email Body Using General Search
Many investigators depend on actual words written in an email, not only the subject or sender. General search also lets you search for an email body by selecting Email.Body, then choosing Contains operator, and entering term you want to find.
For Clarity on this Email Search technique: An Investigator examining discussions in large email data regarding financial risk. He may search for terms such as:
- Risk
- Daily
- Summary
- Market
- Report
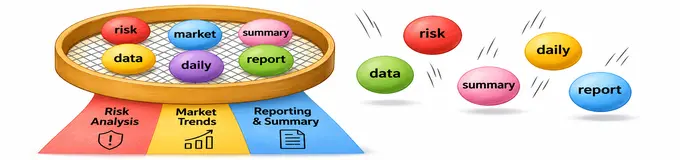
These terms can be arranged into groups to make search more specific.
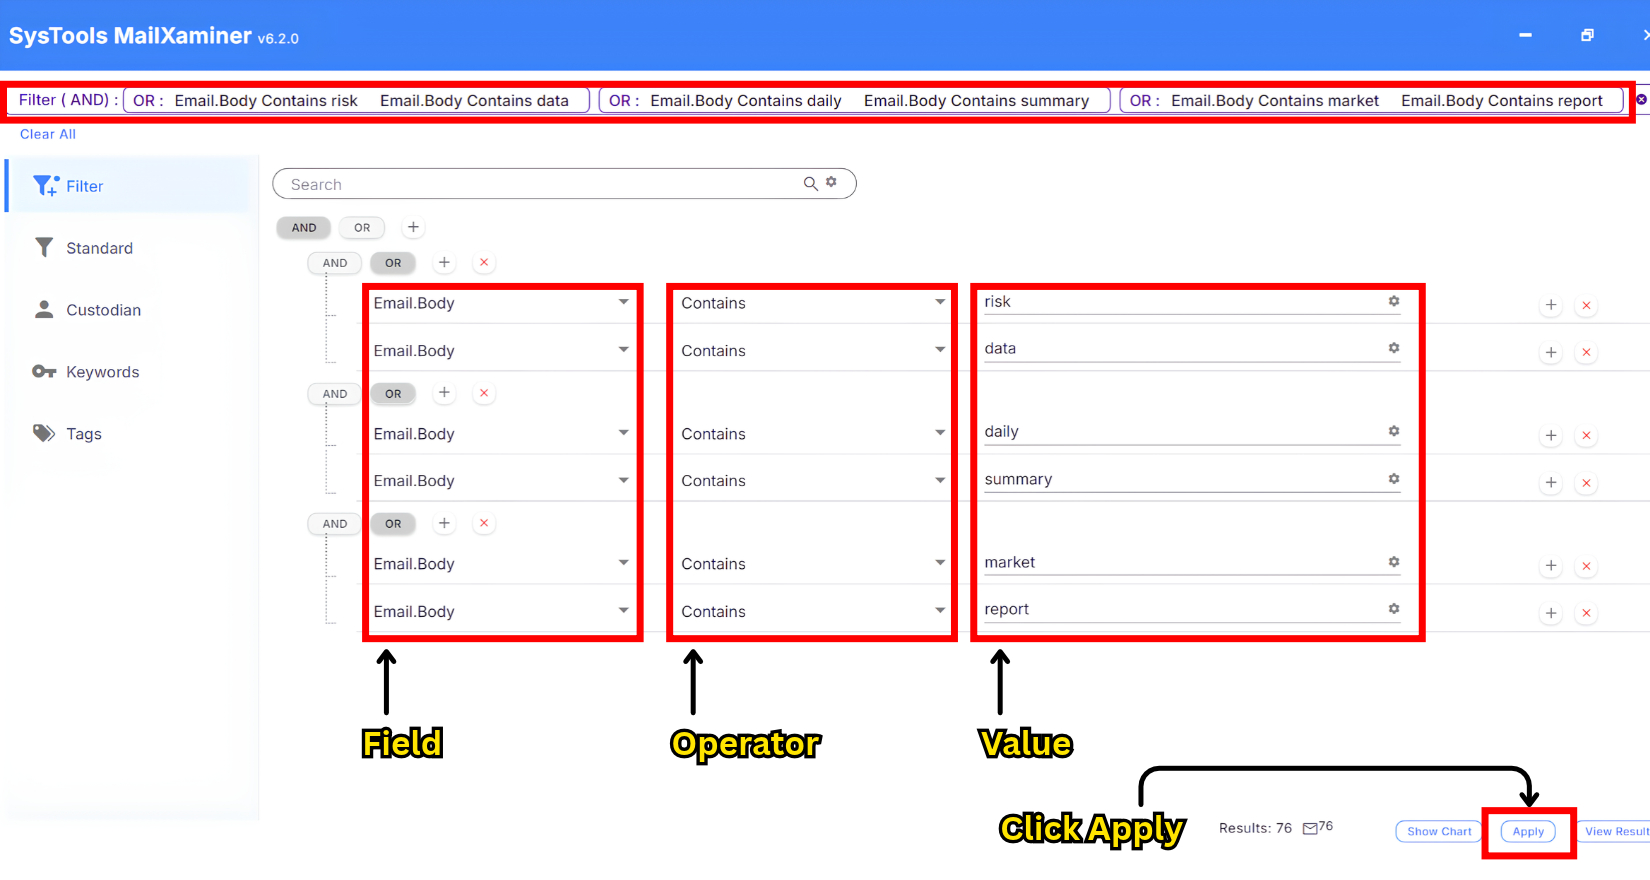
Once this is selected as shown in screenshot and apply button is clicked. Matching emails can be opened and reviewed. Example below shows matching words are highlighted in an email body. This will help investigator locate relevant passages without reading every message from beginning to end.
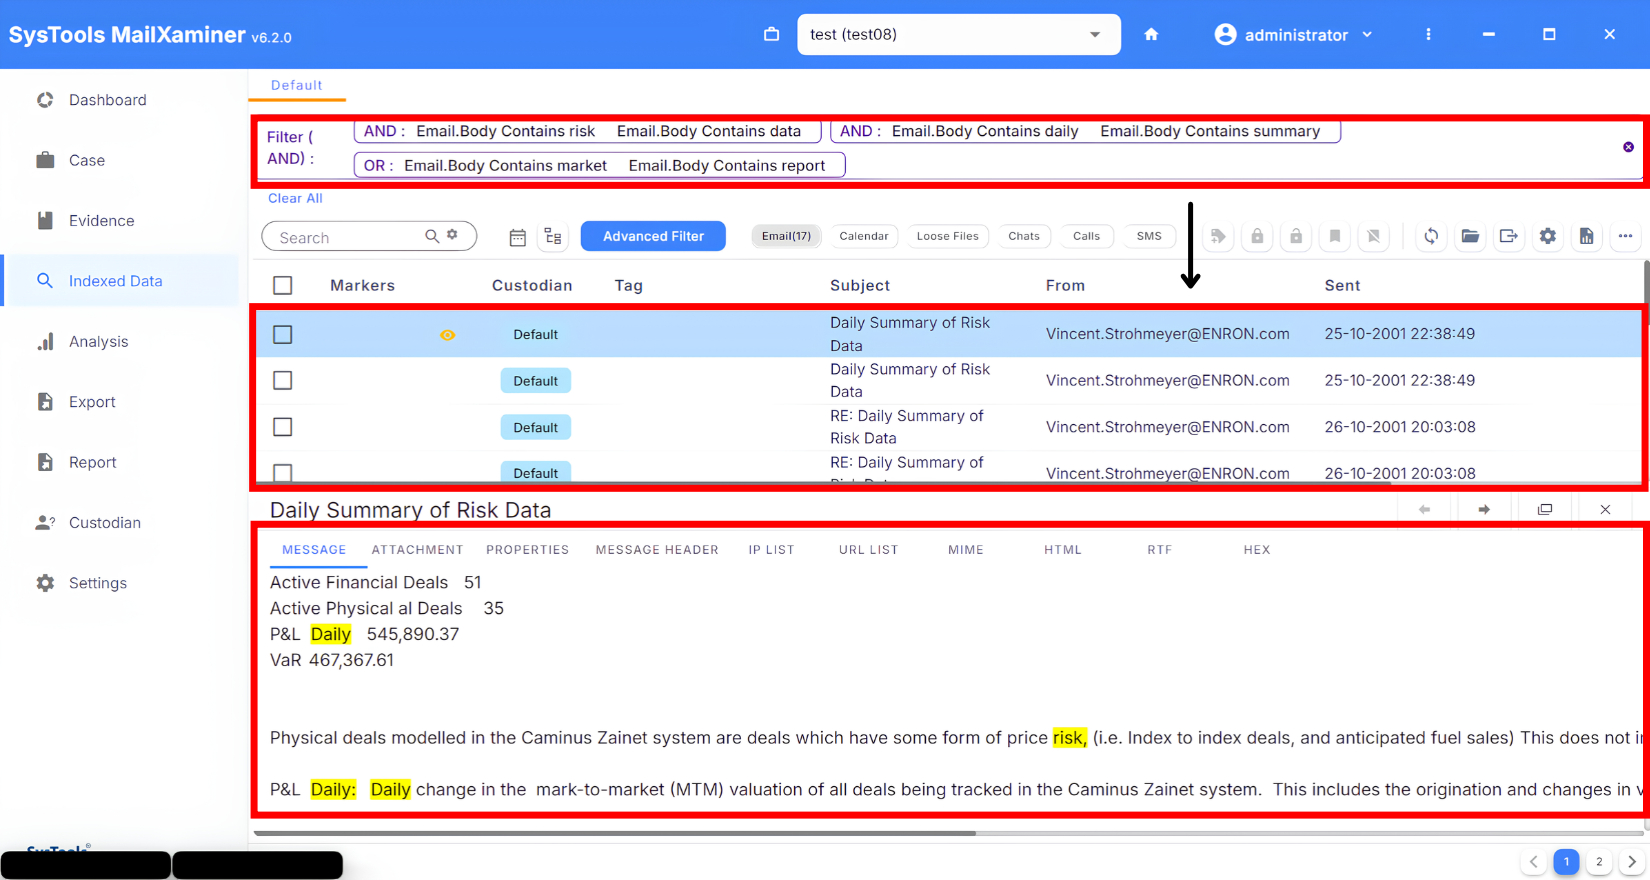
Searching email body is useful when important information is in message text and not in subject line or other metadata field. Matching word do not automatically make message relevant. Read surrounding text and examine context before drawing conclusions.
User or investigator can make this powerful forensic email search mechanism more precise and sharp by combining conditions. To do this correctly, it is important to understand how AND, OR and groups work together.
Type 3: Advanced Query Building With AND, OR, and Groups
AND, OR, and groups let you combine multiple conditions into structured query. AND requires connected conditions to be satisfied together, while OR allows a match when at least one connected condition is satisfied. You can create a group by clicking plus (+) icon and selecting Add Group. You can then add conditions inside it and select logical operator that connects them. Think of a group as a checklist. Each condition is one requirement, and the operator determines how those requirements work together.
AND, OR and Groups let you as MailXaminer operator combine multiple conditions in structured query.
Note:
AND requires connected conditions to satisfied together.
OR allows match when at least one connected condition is satisfied.
You can create group by clicking plus icon near AND, OR and selecting Add Group.
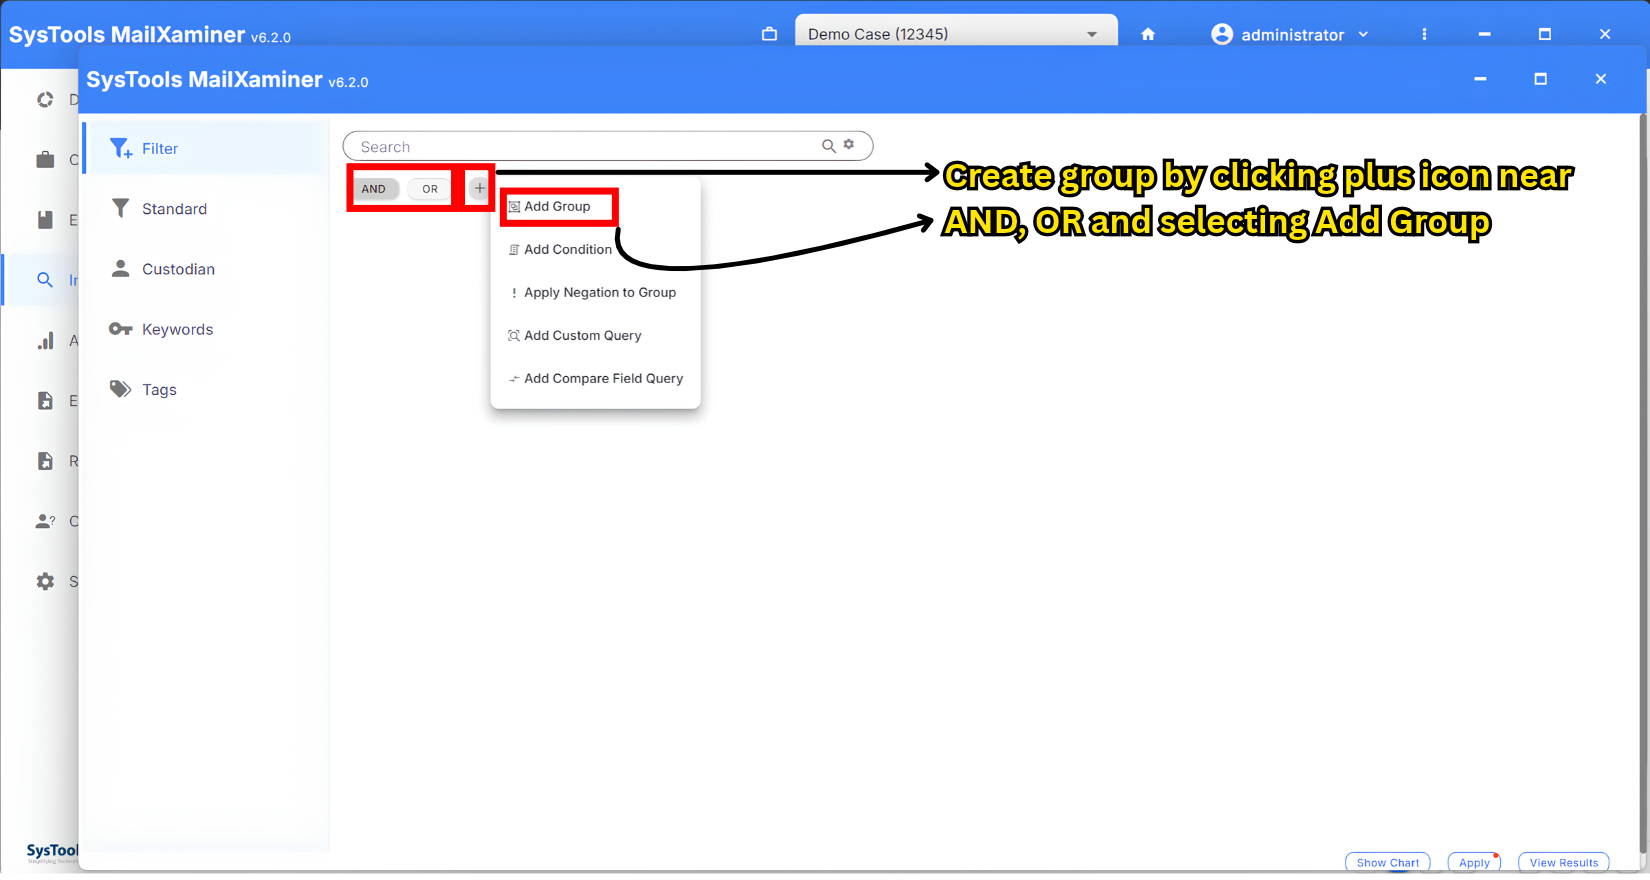
Think of this group as checklist. Each condition is one requirement, and operator determines how these requirements work together.
When to use AND: Use AND when every connected condition is to be satisfied. For instance, As an investigator you want to find emails that have at least one attachment and whose attachment name contains invoice.
The query will contain these two conditions:
- Attachment count is greater than or equal to one.
- Attachment name contains invoice.
When connected by AND, both conditions must be met then only email will qualify under that group.
When to use OR: Use OR when different conditions can independently identify relevant email. For instance, you are looking for emails whose attachment name contains invoice or whose attachment OCR text contains invoice. Under OR logic, email can qualify by matching either condition.
How Do Nested Groups Work
Nested groups allow users combine related search conditions into different groups, within one query. For example, one group can look for emails containing both risk and data. Another look for emails having both daily and summary. You can use AND or OR, to decide how these groups work together. Think of each group as small checklist. First this Email Forensics Software checks conditions inside each group. Then it combines group results using selected outer operator. AND: required email to meet requirements of both groups. OR: allows it to match either group.
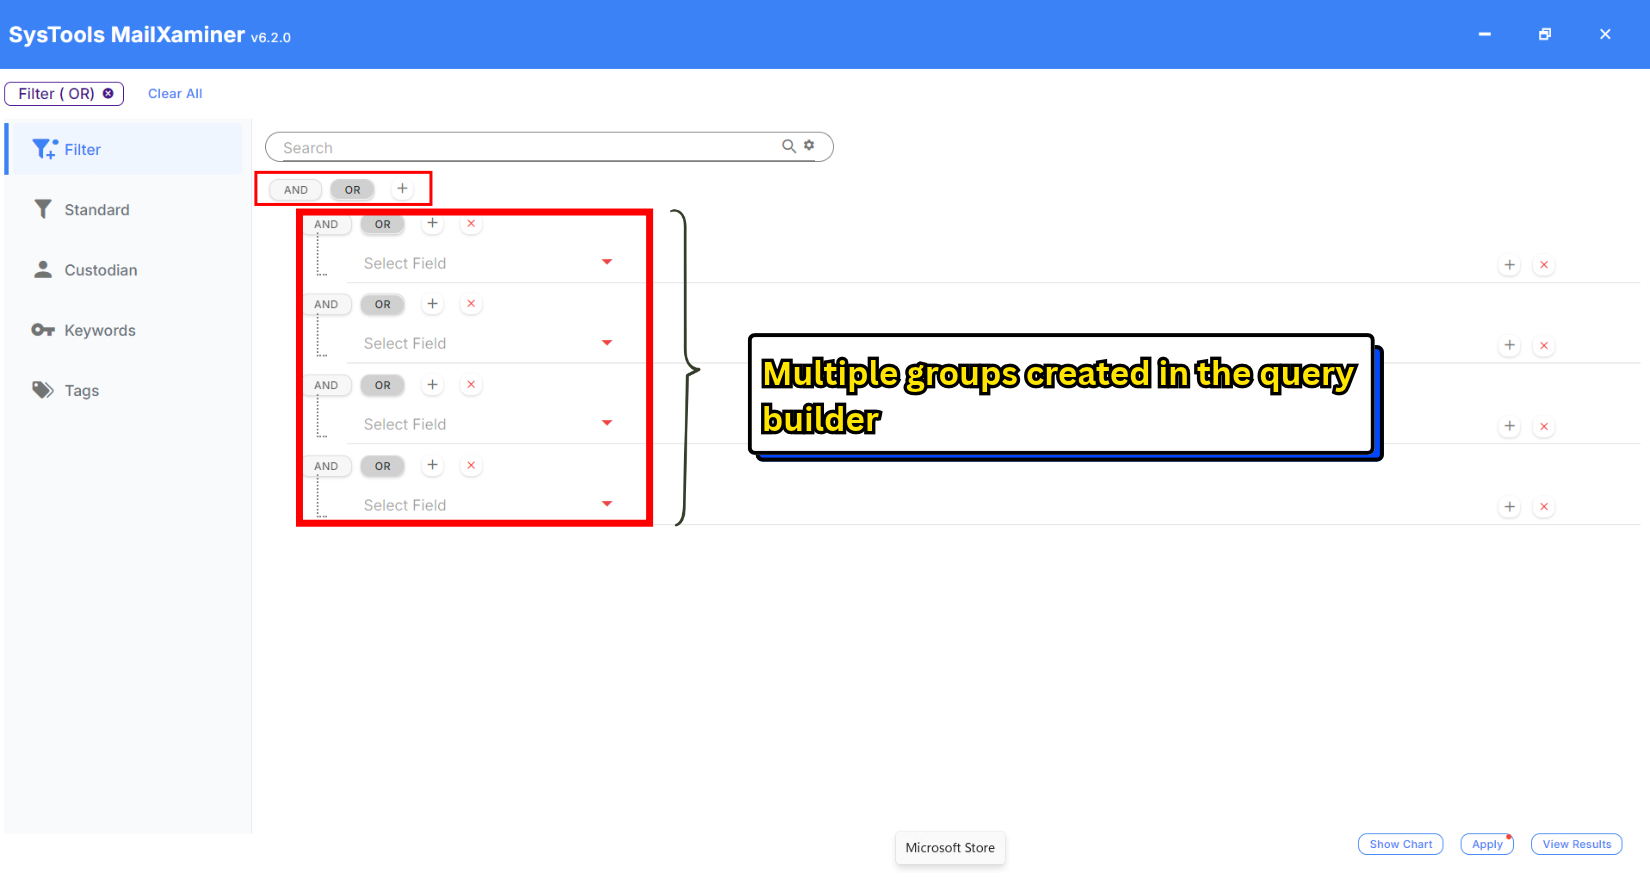
Example: How AND and OR changes email-search
Consider Search using three groups of email-body conditions:
- Group 1: Email.Body Contains risk and Email.Body Contains data.
- Group 2: Email.Body Contains daily and Email.Body Contains summary.
- Group 3: Email.Body Contains market or Email.Body Contains report.
When outer query uses AND, an email must satisfy all three groups. If first two groups use AND internally, email must contain both risk and data, both daily and summary and at least one market or report. On test dataset. This query returned 17 emails.
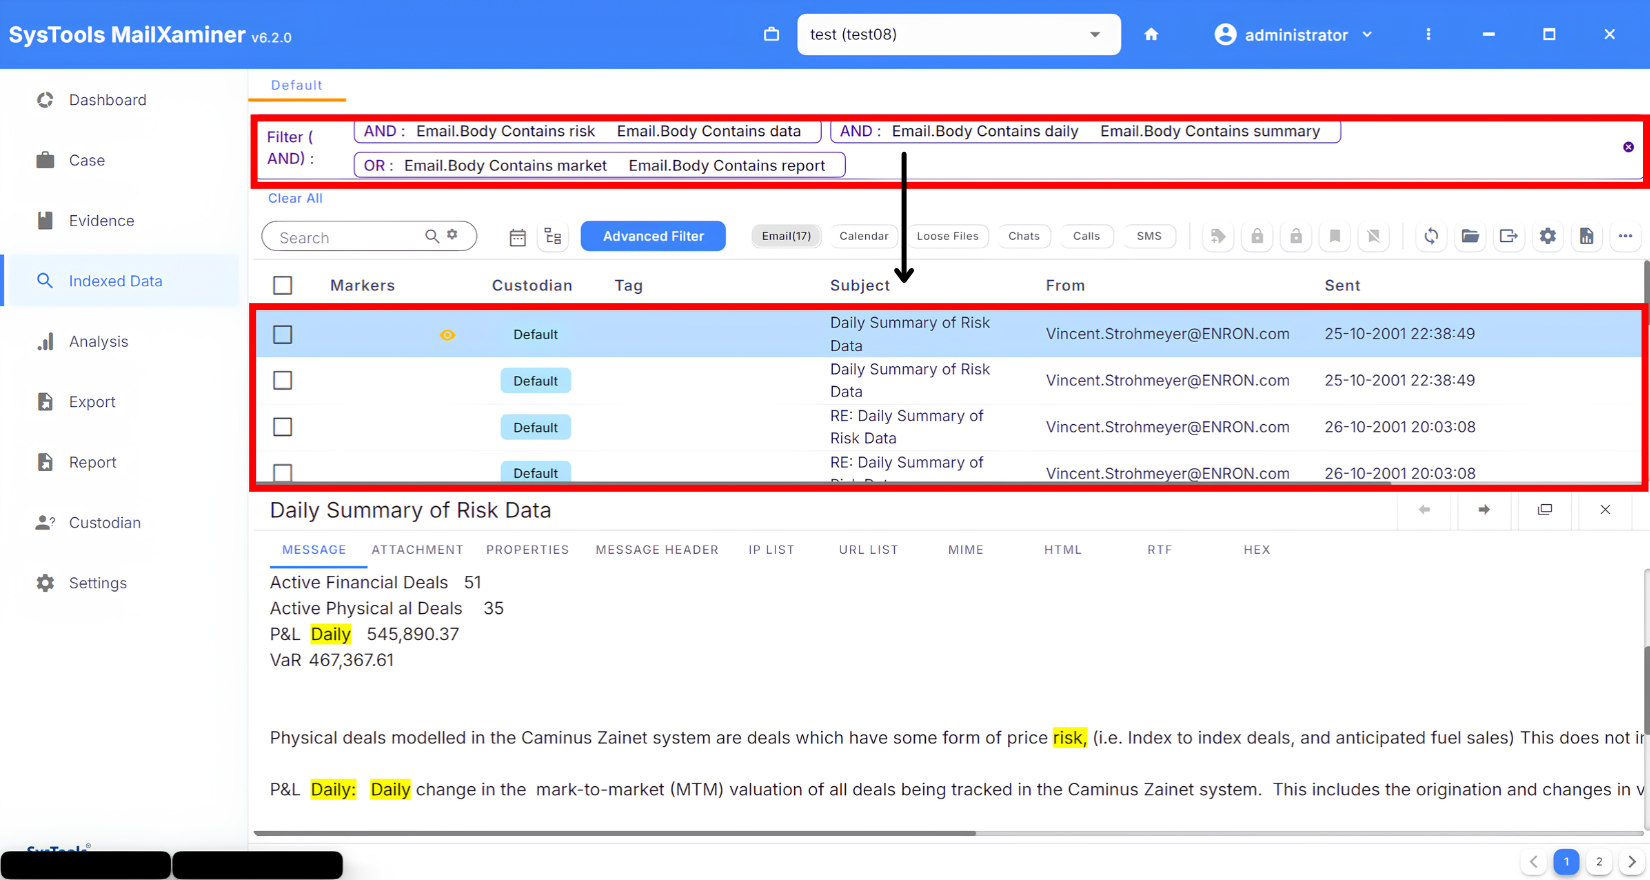
Now think of two-group query, where first group will use AND and second group will use OR, while keeping AND between the groups.
First group required an email to contain both: Risk and Data.
Second group accepts either Daily or Summary.
Since both groups are connected by AND, the result that this tool will deliver have to satisfy both group-level conditions. In this supplied test dataset. This query returned 42 emails.
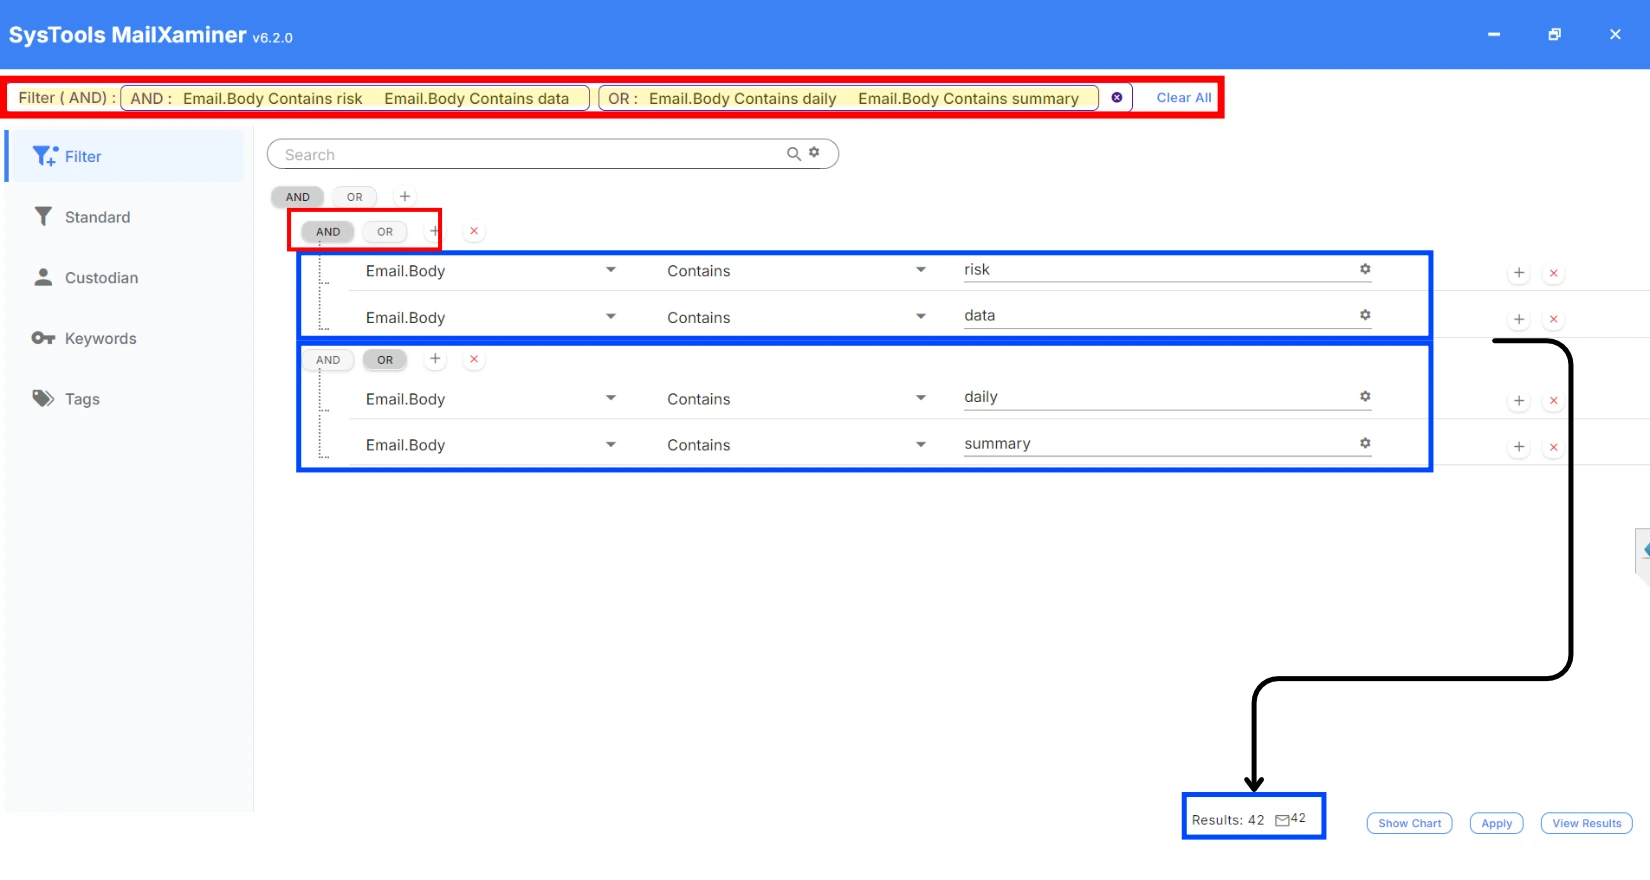
Note: Key lesson is that AND and OR is for more than changing number of search results. They change requirements email must meet to qualify. Before application of complex query, review operator inside every group as well as operator connecting groups.
Creating Search Using Add Custom Query
This tool also provides Add Custom Query option in General Search. It allows investigators and users to enter multiple search conditions as structured query expression instead of adding and inserting each condition individually through Query Builder interface.
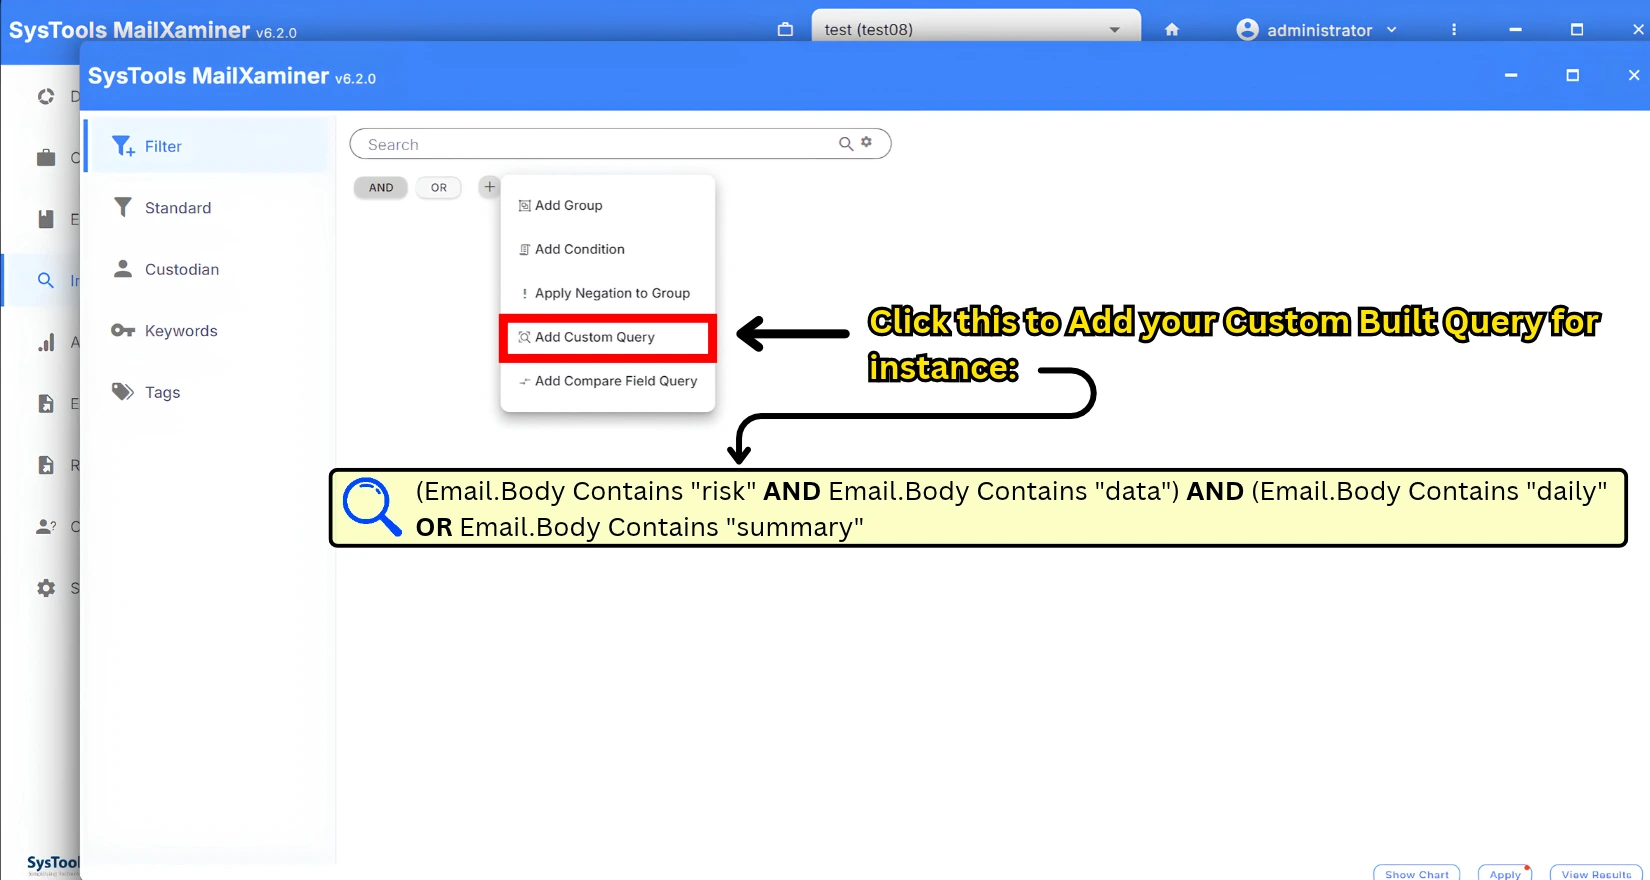
Take this query for example:
(Email.Body Contains “risk” AND Email.Body Contains “data”) AND (Email.Body Contains “daily” OR Email.Body Contains “summary”)
This query has two groups of conditions:
- First Group: Email body must contain both “risk” and “data”.
- Second Group: Email body must contain “daily” or “summary”.
Both groups are connected using AND, that means email must satisfy conditions in both groups to qualify to be present in delivered result.
Building Query With Multiple Groups
You can extend same principle to multiple groups when your investigation requirement demand more complex email search techniques. For example, an investigator can use multiple groups that help examine:
- Emails with at least one attachment and an attachment name containing invoice.
- Data whose available attachment OCR text contains relevant term.
- Emails whose BCC field matches address under investigation.
- Another condition selected according to the case requirements.
Note: These conditions are for explanation. Choose actual fields and values based on evidence and investigative question.
If four groups are connected by AND, a matching email must satisfy all four groups. If they are connected by OR, an email can qualify by satisfying any one of those groups. More complex combinations are possible, but every additional condition should serve a clear investigative purpose.
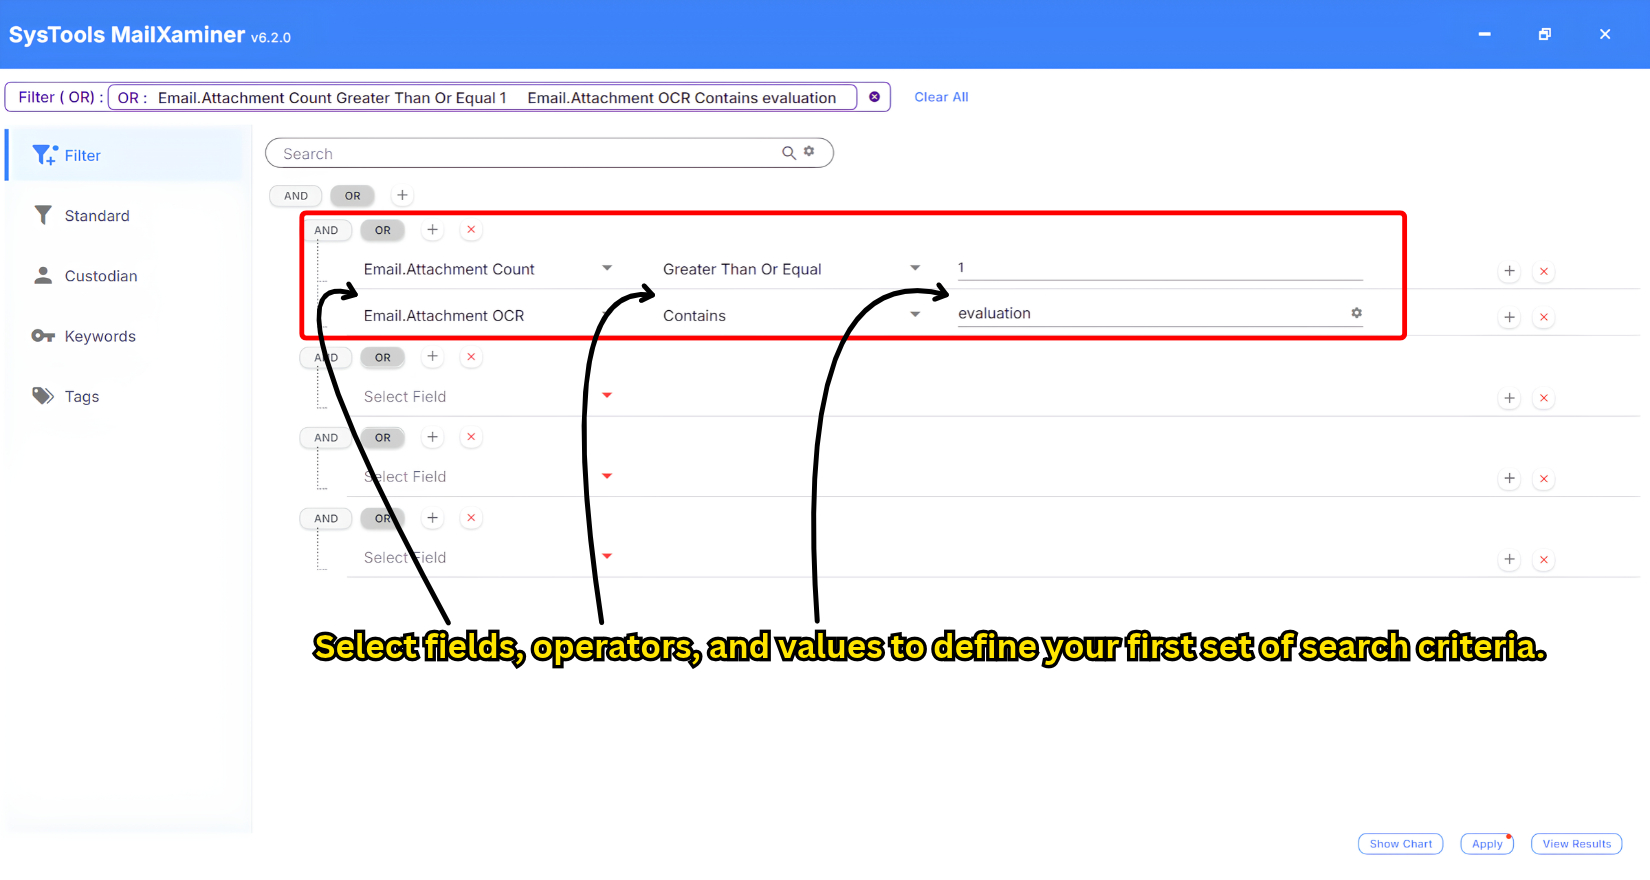
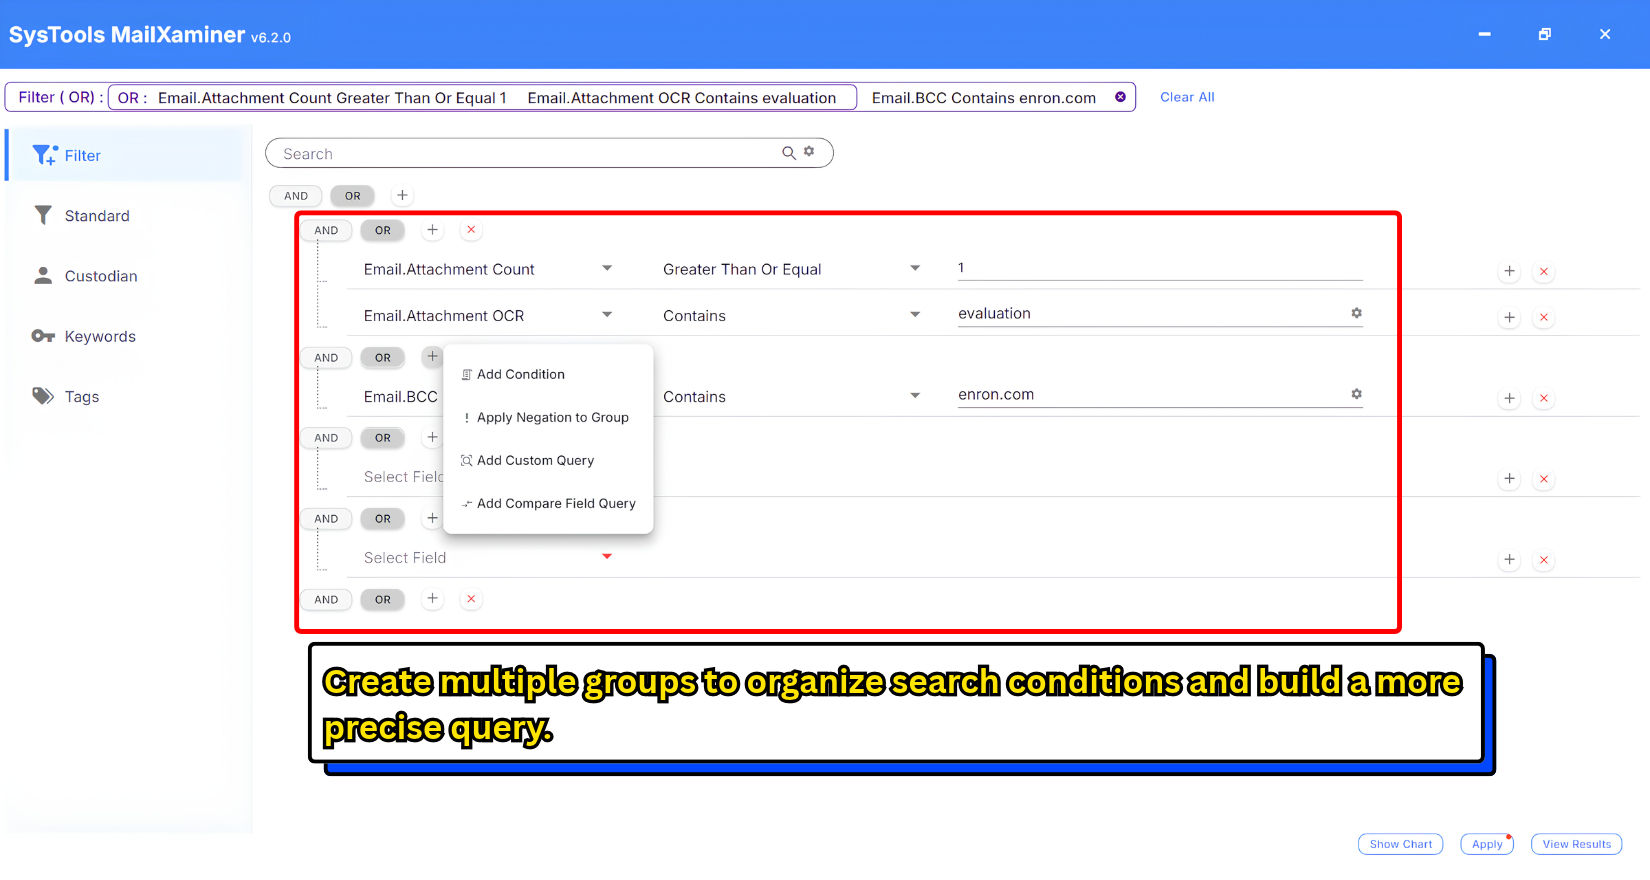
As we continue to build this query using this Email search technique, the strip at top reflects conditions and groups you have added. Review structure before applying search, especially when you have combined different operators.
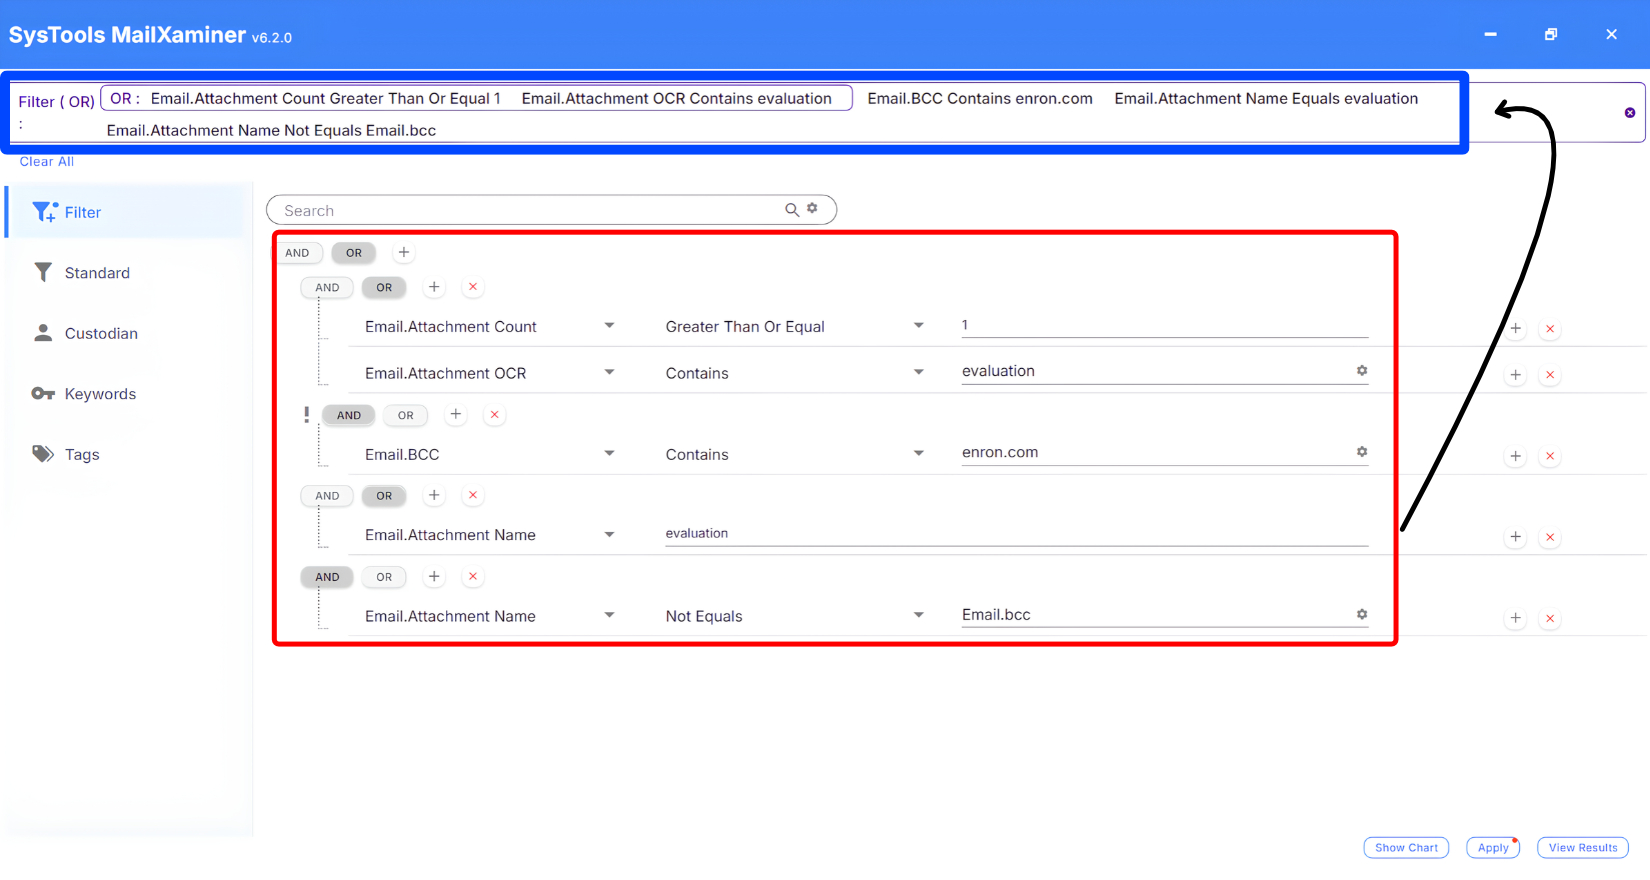
Final Step: Apply Your Query and Troubleshoot Search Results
Once query is built through General Email search technique and is complete. Check:
- Selected fields
- Values
- Operators
- Group logic.
Click Apply to run the search, then review results to determine do the results satisfy your investigative question. Query builder’s additional actions can support more targeted and focused searches. Each should be used with understanding of its behavior.
- Apply Negation to Group: Reverses matching logic of selected group. Check resulting query carefully as negation changes which email qualify.
- Add Custom Query: Lets you add custom query using supported syntax. Confirm syntax and expected behavior before relying on the result.
- Compare Field Query: Provides way to construct field comparison query. Check available fields and comparison controls to ensure that comparison expresses intended condition.
What If Your Search Does Not Return Expected Results
Use following checklist to identify most likely issue before rebuilding query from scratch.
| Problem | What to Check |
|---|---|
| No Emails were Extracted | Confirm that evidence is indexed and your fields, values and conditions are appropriate. |
| Too many emails are returned | Add more relevant conditions or use AND where all requirements must be met. |
| Relevant Emails seem to be missing | Review your search terms, selected fields, indexing coverage and group logic. |
| Results are broader than expected | Check whether OR, allows emails to qualify through alternative conditions. |
| Emails are excluded unexpectedly | Review negation and confirm how groups are connected. |
Search that do not provide you any results, do not prove that evidence is absent. Reason can be like query is too restrictive, wrong field may have been selected, relevant information may not be available in indexed content. Similarly, large result set do not automatically mean search has failed. It is a useful starting point that demands refinement.
After application of query, examine matching result, for investigative work, document important query settings and reason for using specific Email search technique so search can be reviewed and understood later.
Wrapping Up
Well-structured search helps you focus on relevant evidence. Every result needs careful review, if your search results returns no results, check your query and indexed data before concluding information is absent. MailXaminer provides six search methods that support different search goals and General Search is practical starting point when you need to find emails by keyword or build more detailed query using different conditions.
Frequently asked questions
Q: Can I search for words inside an email body?
A: Yes, Select, Email.Body, field and Contains as an operator and enter term that you want to find. User can combine multiple body-text conditions using AND/OR logic to narrow or broaden the search.
Q: Should I use AND or OR?
A: Investigator should use AND when all connected requirements must be met. Usage of OR is when any one of connected conditions can qualify an email. If you combine groups, review operator at both group and outer query levels.
Q: Why should I review emails after applying query?
A: Query identifies email that match its conditions. Reviewing messages helps you determine whether results are relevant or search needs further refinement.
Q: How to make Email Searches More Effective
A: Effective Email search techniques for Digital Forensics begin with one clear investigative question and search that matches it. Start with keyword, introduce field based conditions when needed and use groups and logical operators to organize more complex requirements.